

PacketSanitizer is a native C plugin that integrates directly into Wireshark’s engine — no Python, no Lua, no external dependencies. It sanitizes packet capture files at wire speed with three modes to suit different security needs.
Screenshots
Menu
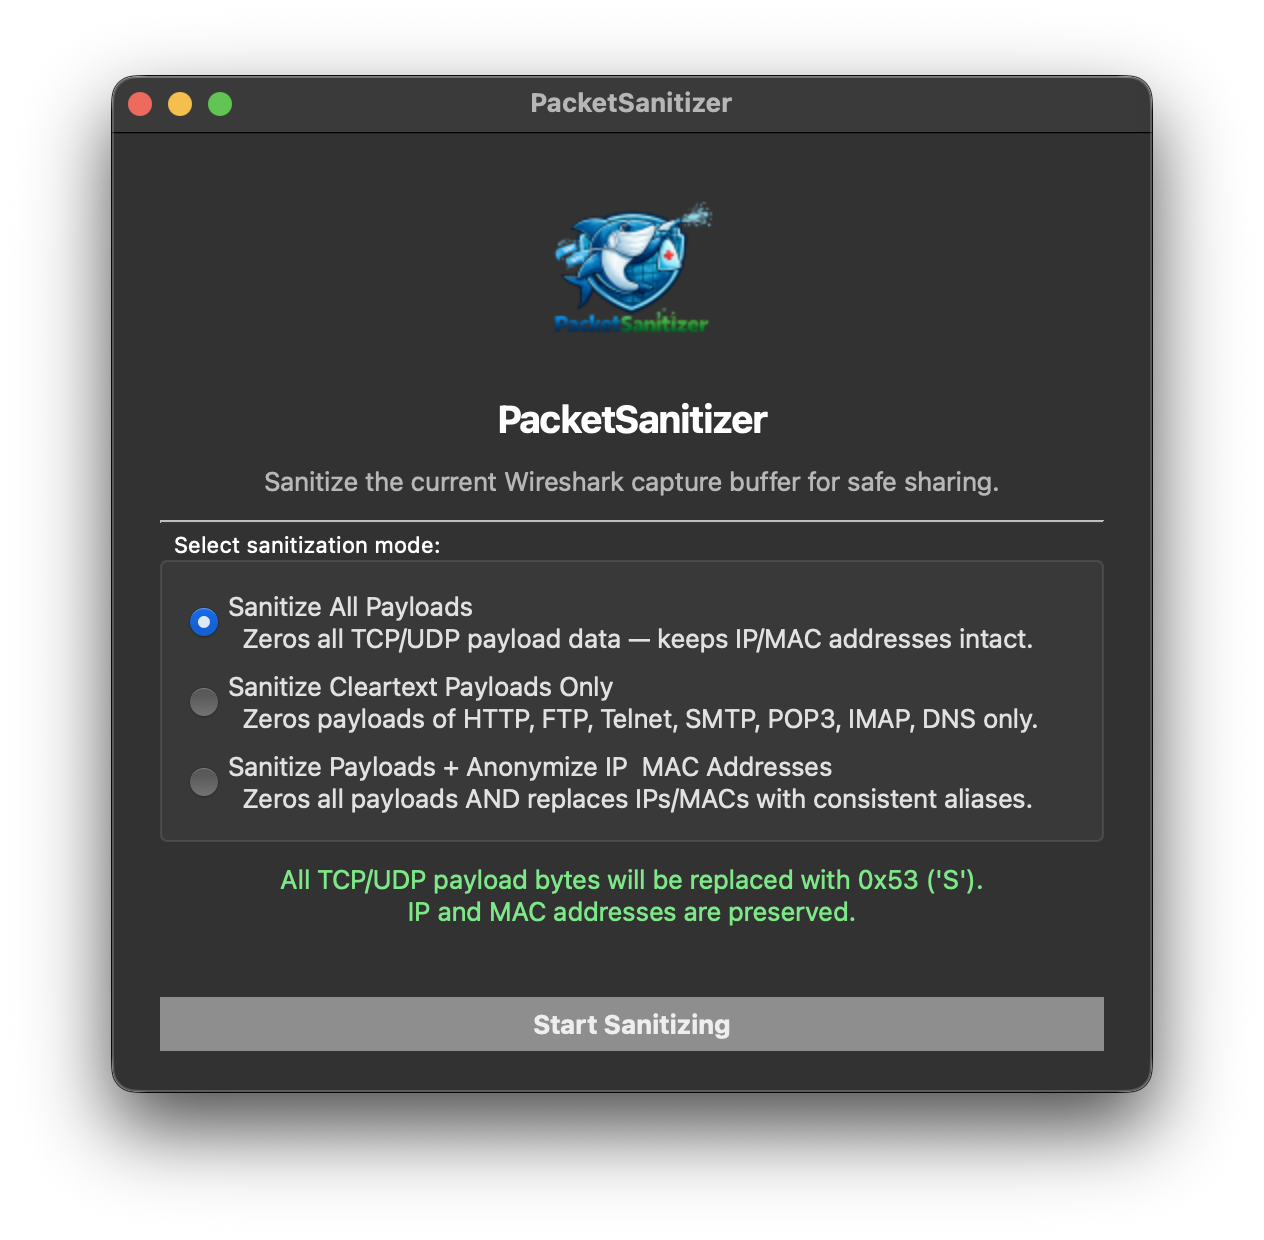
Access via Tools → PacketSanitizerPro → Open PacketSanitizerPro…
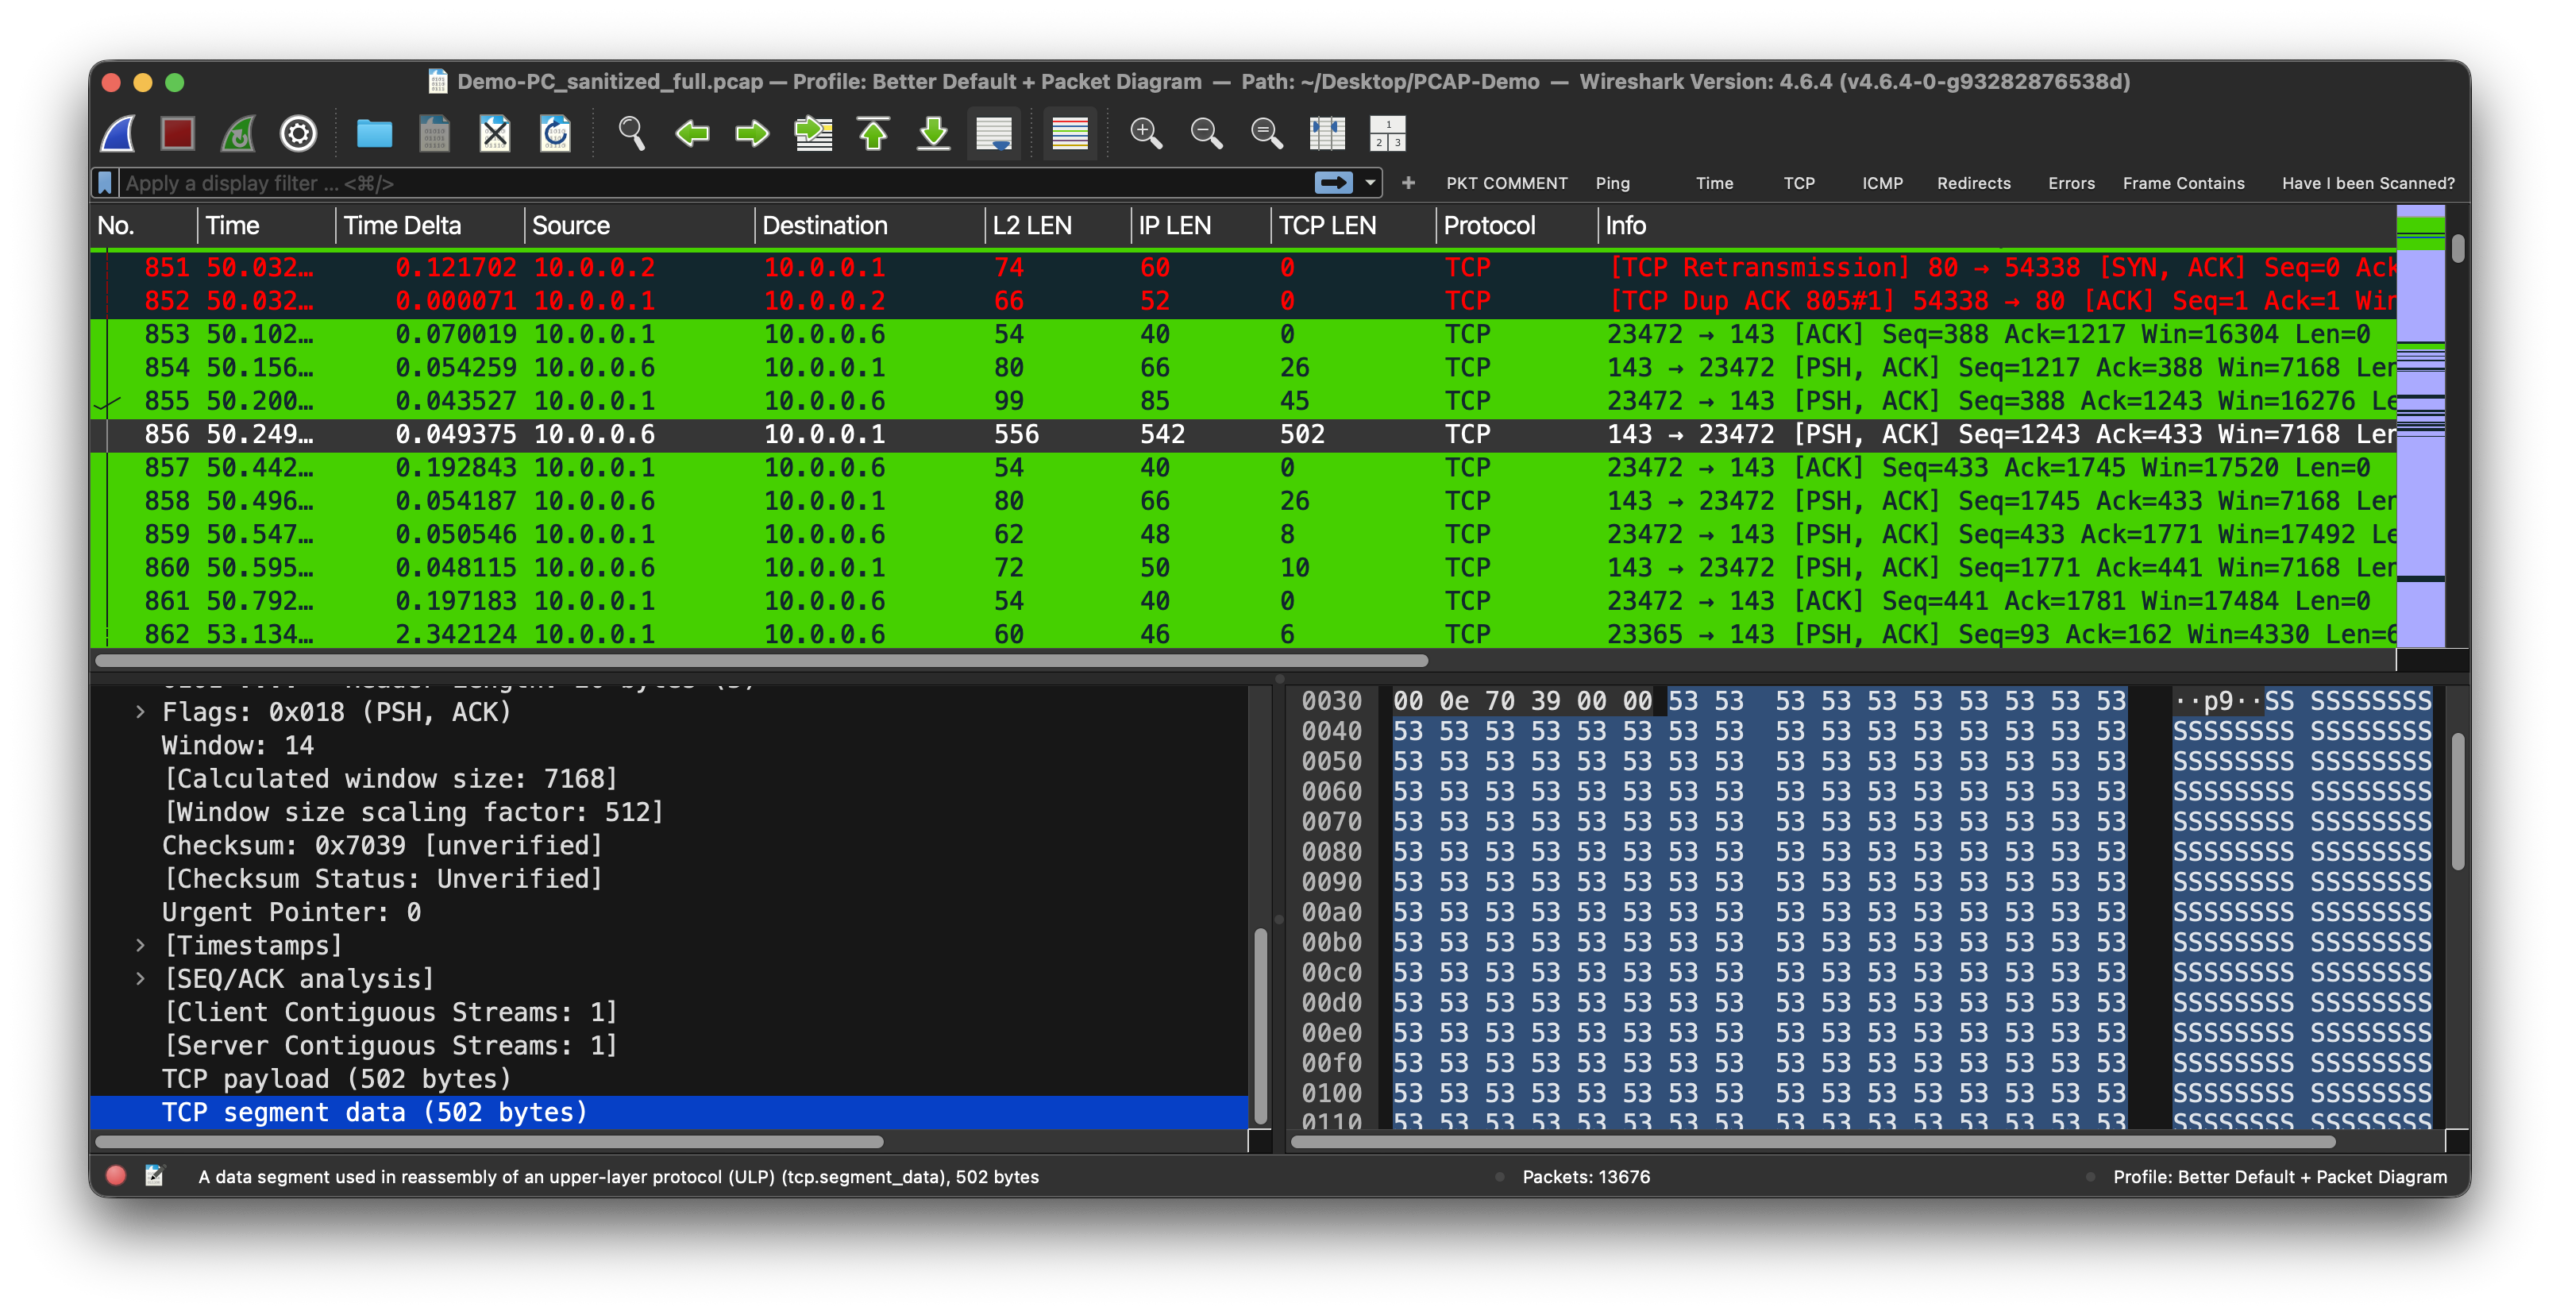
Before sanitizing
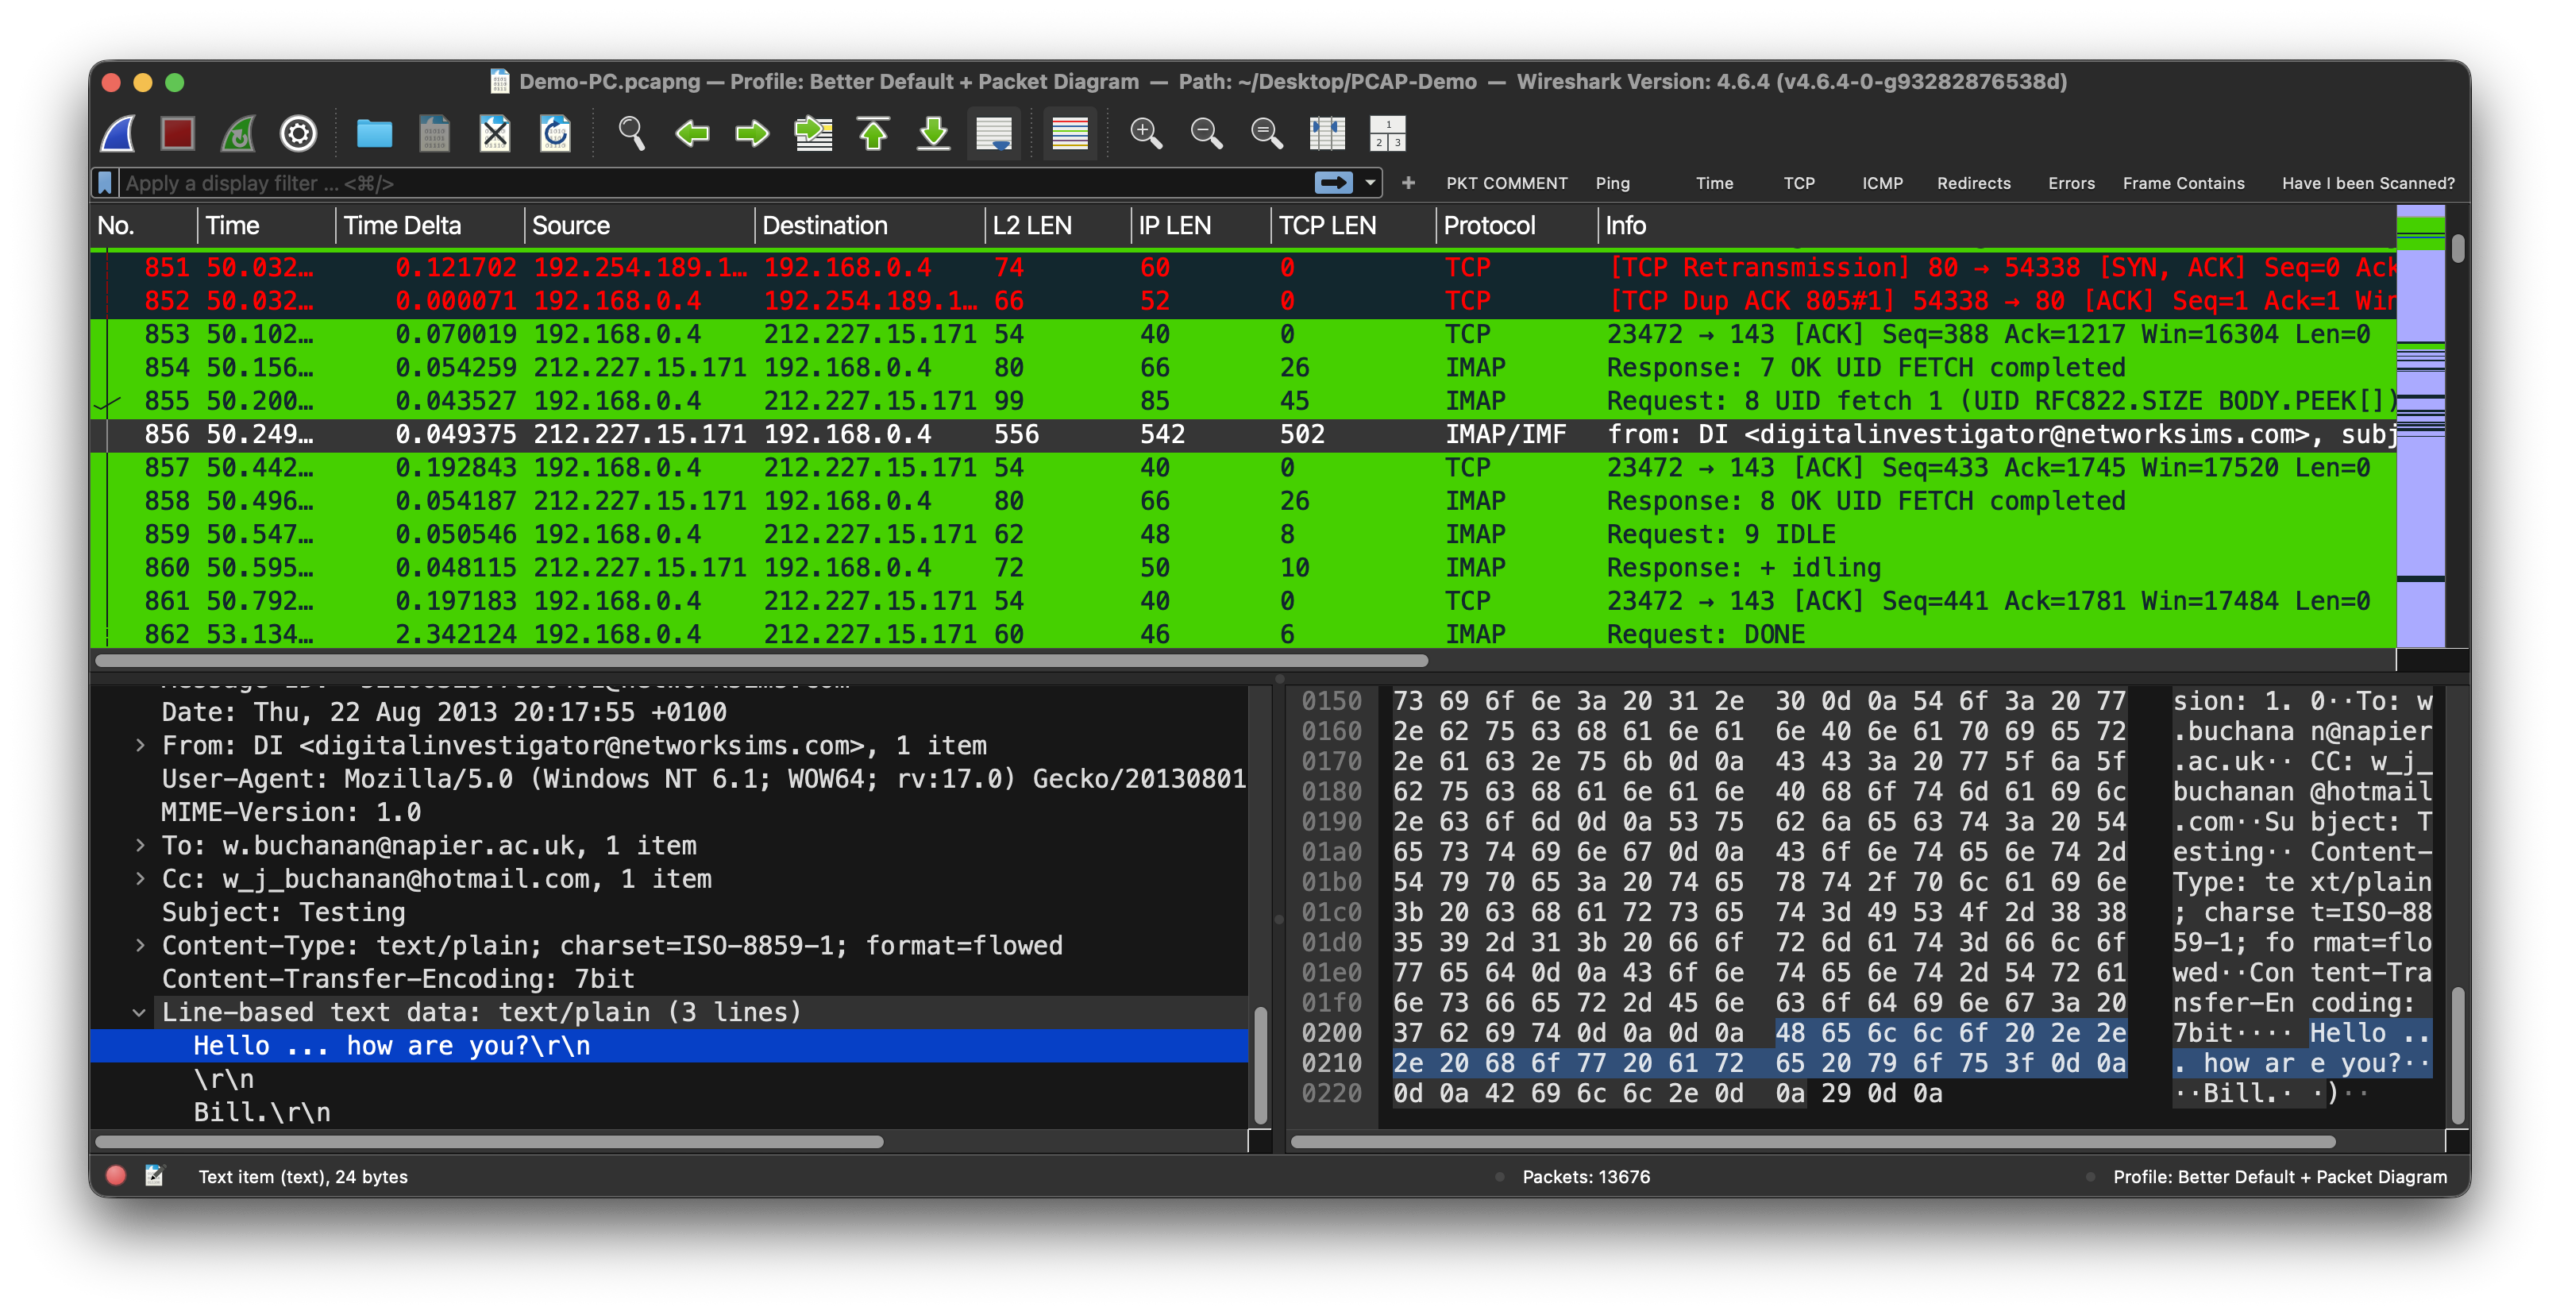
After sanitizing
Sanitization modes
| Mode | Sanitized | Preserved | Use case |
|---|---|---|---|
| 1 — All payload | All TCP/UDP/ICMP payloads | IP & MAC addresses, headers, ports | Remove payload while keeping topology visible |
| 2 — Clear-text payload | HTTP, FTP, Telnet, SMTP, POP3, IMAP, DNS payloads | Encrypted traffic, IP & MAC addresses | Remove sensitive clear-text data, keep encrypted traffic analyzable |
| 3 — Payload + IP & MAC | All payloads + IP + MAC addresses | Protocol structure, ports, timing, flows | Maximum sanitization for external sharing |
How it works
PacketSanitizer links directly against libwireshark and libwiretap, with a Qt dialog for the UI. It opens the capture via the wtap read API, parses Ethernet → VLAN → IPv4/IPv6 → TCP/UDP/ICMP for each packet, applies the selected sanitization in place, recomputes IP/TCP/UDP checksums, and writes the result via the wtap write API.
- IP anonymization: deterministic mapping into
10.0.0.0/8, same original IP always maps to the same anonymized IP - MAC anonymization: locally administered
02:00:00:00:00:XXaddresses - Payload sanitization: replaced with a recognizable
0x5341(“SA”) pattern, packet size preserved
Installation
macOS (universal): cd installer/macos-universal && chmod +x install.sh && ./install.sh
Linux (x86_64): cd installer/linux-x86_64 && chmod +x install.sh && ./install.sh
Windows (x86_64): cd installer\windows-x86_64 && install.bat
Installers detect your Wireshark version and plugin directory, install to your personal plugin folder (no admin required by default), and offer to uninstall a previous version if detected.
Requirements
- Wireshark 4.6.x
- Qt 6.x runtime (bundled with the official Wireshark installer on macOS/Windows; on Linux:
sudo apt install libqt6widgets6) - VC++ 2022 Redistributable on Windows
Security notes
The sanitized file removes sensitive data but still contains protocol headers and structure, packet timing information, and port numbers/protocol types. Review the sanitized file before sharing to confirm it meets your organization’s requirements.
License
GNU General Public License v2.0 — see LICENSE.
Acknowledgments
The Wireshark development team for the epan plugin API, wtap read/write framework, and dissector infrastructure; the Wireshark community for documentation and reference source. AI-assisted (Claude by Anthropic) for the native C plugin architecture, Qt UI design, cross-platform build system, installer scripting, and documentation.