Ping the Networker — a jump & run for people who know what STP stands for
This was actually just a quick and dirty fun mini project — but people liked it, so I kept adding more and more. You play Ping, the network engineer of a data hall: run and jump through the racks, fix routers, switches, firewalls, DNS and PC settings, then press Send and watch the packets travel (and the ACK come back).
Not sure where it belongs: arcade game or education? It can be a good learning tool for kids and for adults who love games — but a fair warning: it is not THAT easy. There are several levels of help (a nudge, a diagnosis, the exact fix) if you get stuck.
- Tickets: each ticket says which client wants to reach which server. The packet takes the colour of the client; the server wears the colour of the destination.
- Run & collect: collect a diamond to unlock a device, use the green spring pads to reach high ledges, and avoid bugs and sparks.
- Configure: open the unlocked device and fix it — routes and next hops, firewall rules, STP and port security, DNS records, masks, gateways, DHCP, MTU/MSS over an IPsec tunnel.
- Send: packets hop device by device. A drop shows the reason and the culprit; a hostile packet must be blocked.
- Capture: a Wireshark-style analyzer with filters and real hex helps in the later levels — the boss level gives no hints at all.
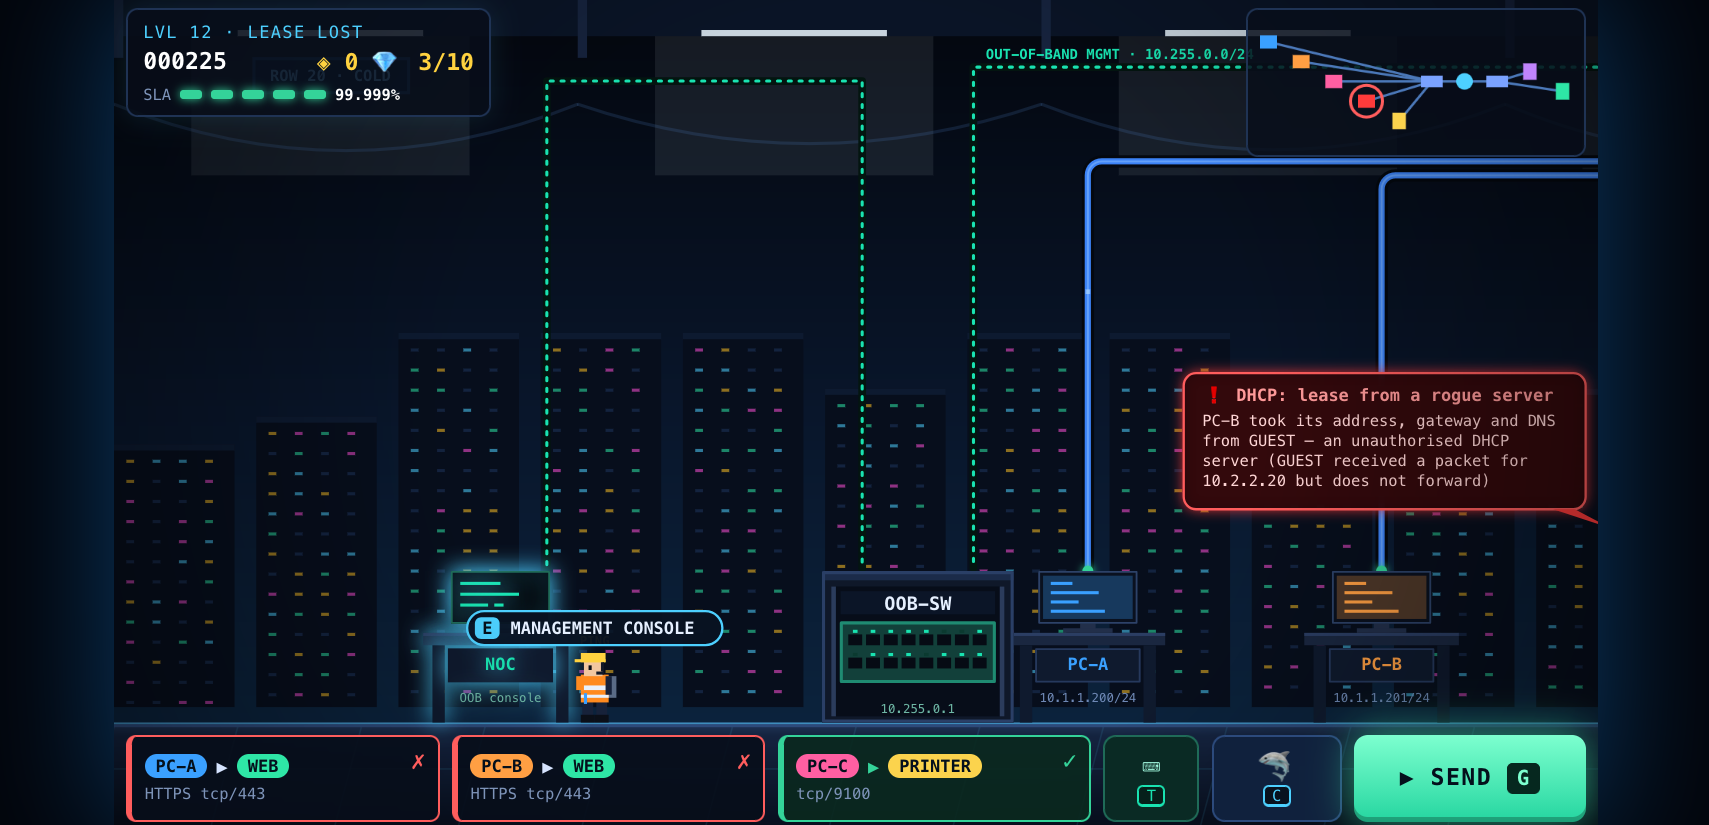
A level: the data hall, the tickets at the bottom, a failing DHCP lease and the NOC desk.
Every switch, router, firewall and server has a separate management port (Mgmt0) on a dedicated out-of-band (OOB) network — the dotted teal cables above the data cables. It is independent of production, so it keeps working when the data plane is broken. That is exactly why real networks have one.
At the start of every hall you find the NOC desk and the OOB switch. Press T (or E at the desk) and you get an SSH-style terminal: ssh R1, then a small Cisco-like CLI with modes, Tab completion, ? help, show running-config, ping and traceroute. The graphical consoles and the terminal share the same state — use whichever you like.
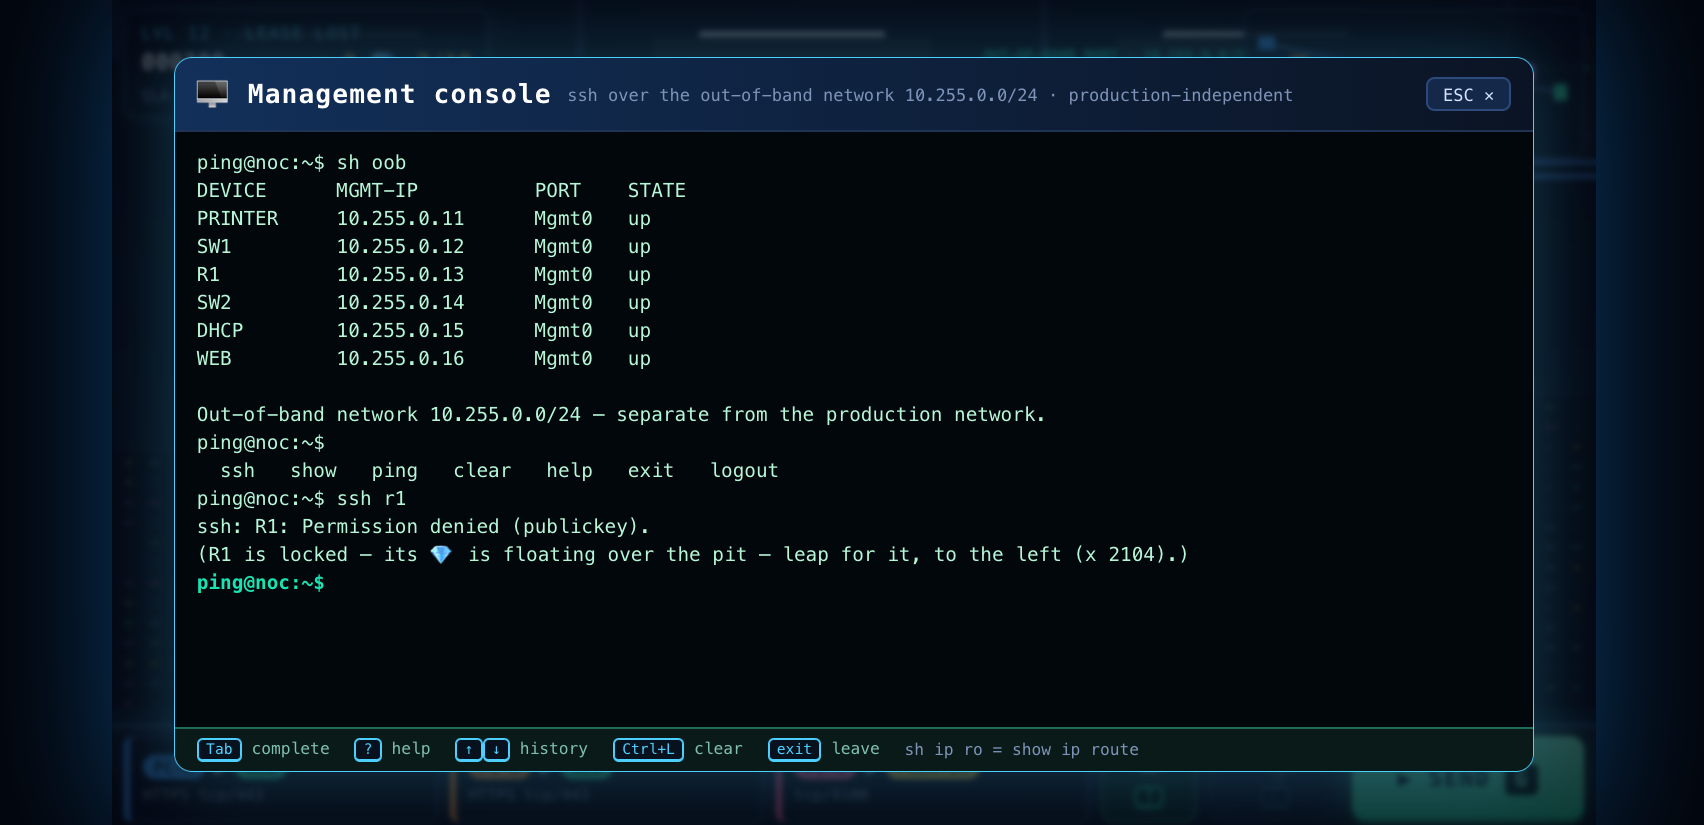
The NOC console: ssh over the out-of-band network. (R1 is still locked — its diamond has not been collected yet.)
14 levels take you from missing static routes through firewalls, spanning tree, port security, TTL and routing loops, IPsec/MTU, DNS, subnet masks, DHCP and a fibre cut to a blind boss level.
Pet Networks (press P on the title screen) are random scenarios on four networks, from a Garage Lab to an Enterprise map: either a factory-blank network you design from scratch, or a running network that broke overnight — fix my network! One to three communications, hidden twists, an optional time limit.
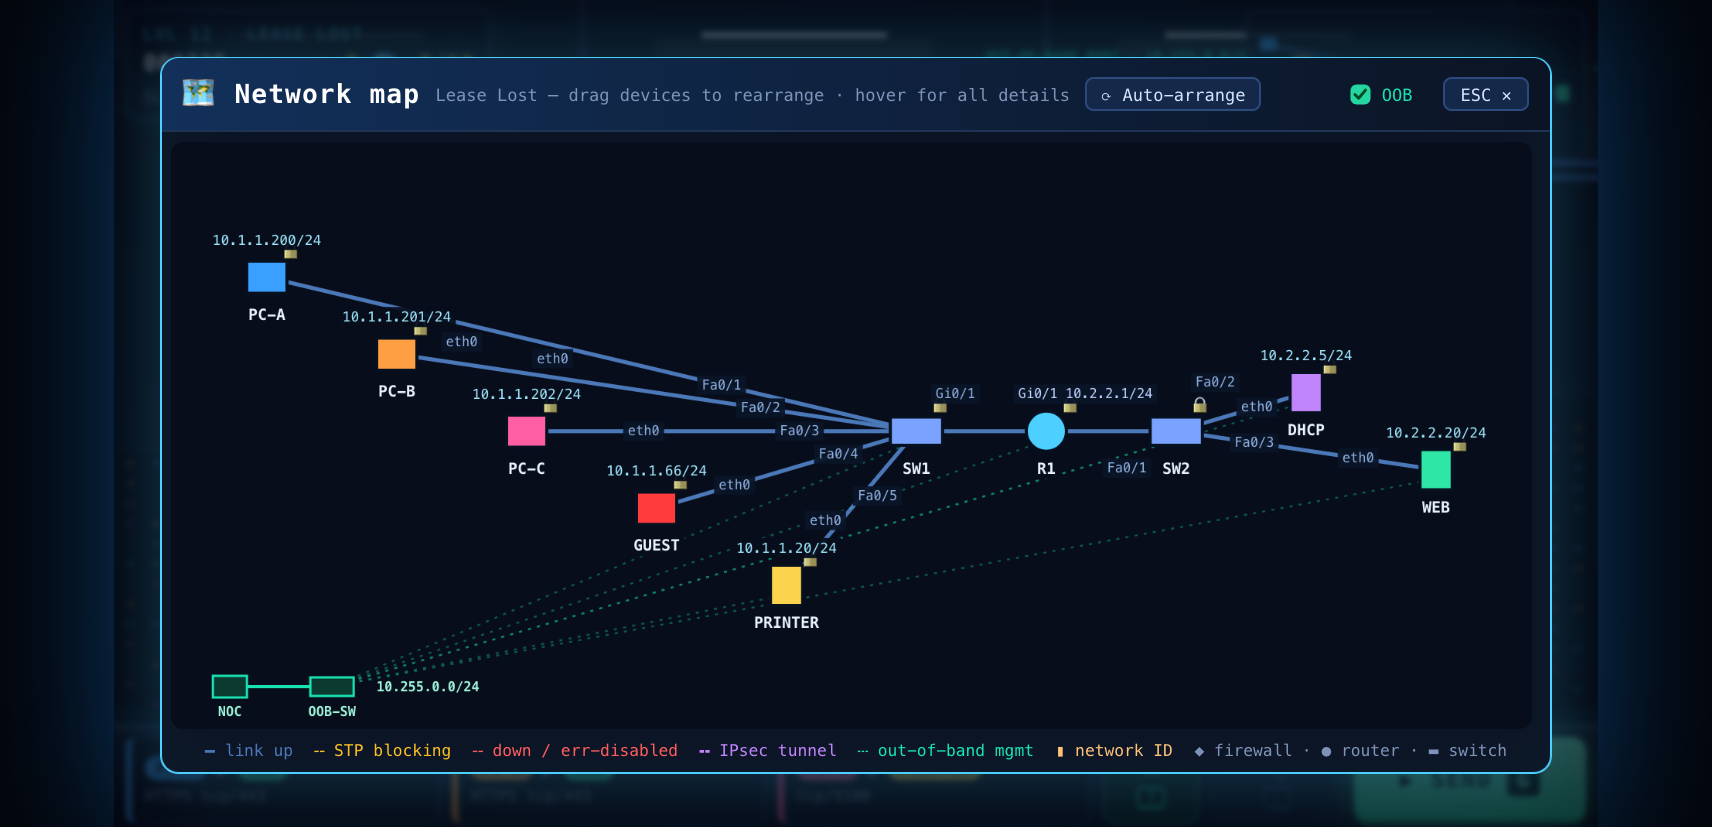
The network map: devices, addresses and ports at a glance — you can drag devices around.
Side note: an iOS version is currently under consideration. It needs a review from Apple, so it may take a while until it is available on the App Store.
PacketCircle 1.3.2 — Light and dark mode, and search for Expert messages
PacketCircle now follows your desktop: choose Dark, Light or System in Settings. Expert messages can be found from the search bar. Available now for macOS, Linux and Windows (signed installer); the iPhone app gets the same Appearance choice with its next App Store release. Still native analysis, on device — not Wireshark.
Sorry about that: the first 1.3.2 release had a bug when searching Expert messages. It is fixed in the latest 1.3.2, build 128 — check the build number under ? / About. If no build number is shown, please download the latest 1.3.2 installer again.
Windows, now signed: the Windows version is identical to the Linux one (same Rust core and interface) and is available to download (64-bit, about 7.5 MB, an .msi inside a .zip). The installer and the app are signed by WLAN GEEKS LLC. Many thanks to Kevin there, who has created some great tools, especially for WLAN troubleshooting: I have the developer account and certificates for Apple (iOS / macOS), but I have had no OV certificate to sign Windows code so far. If I see that people are using PacketCircle, which drives new features and fixes in the app, I will certainly buy the certificate myself. Details in the Linux & Windows User Manual →.
- Dark, Light or System — Settings on the Mac and on Linux / Windows (Options on iPhone) lets you follow the desktop theme or force light or dark, whichever way your desktop is set.
- The Circle and the Infrastructure Map stay black; text, icons, lists and charts are adjusted so they stay readable in light mode.
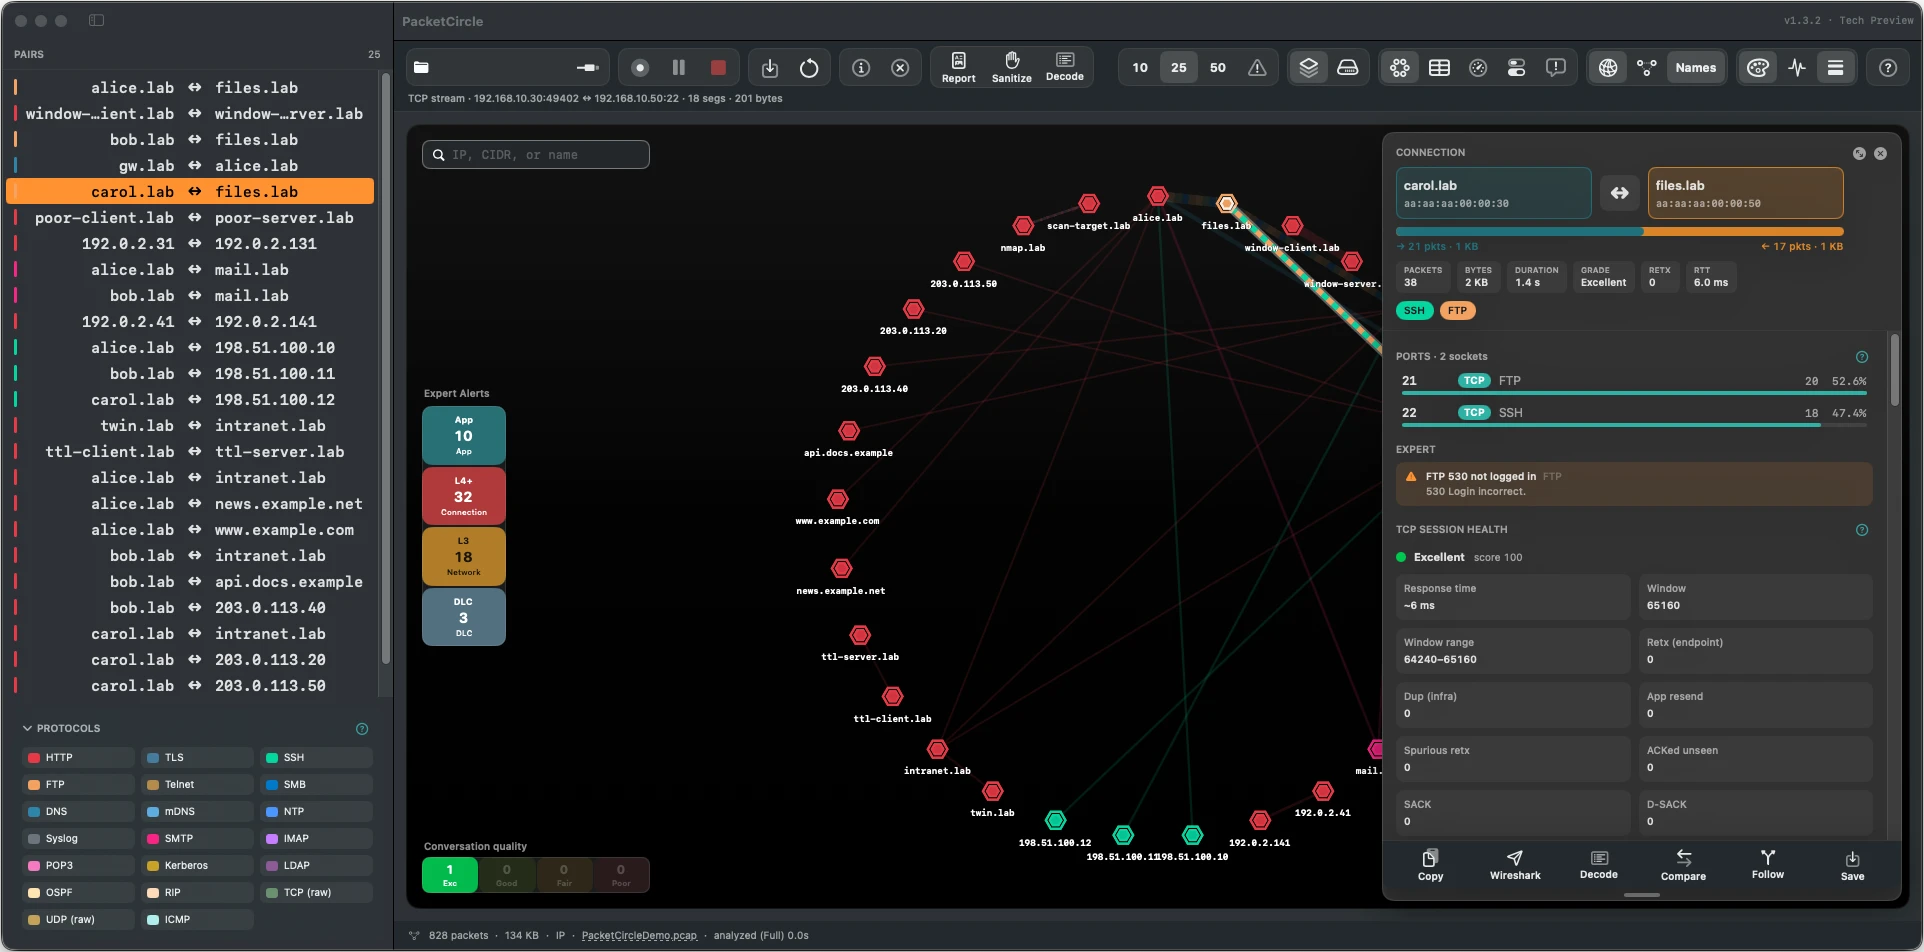
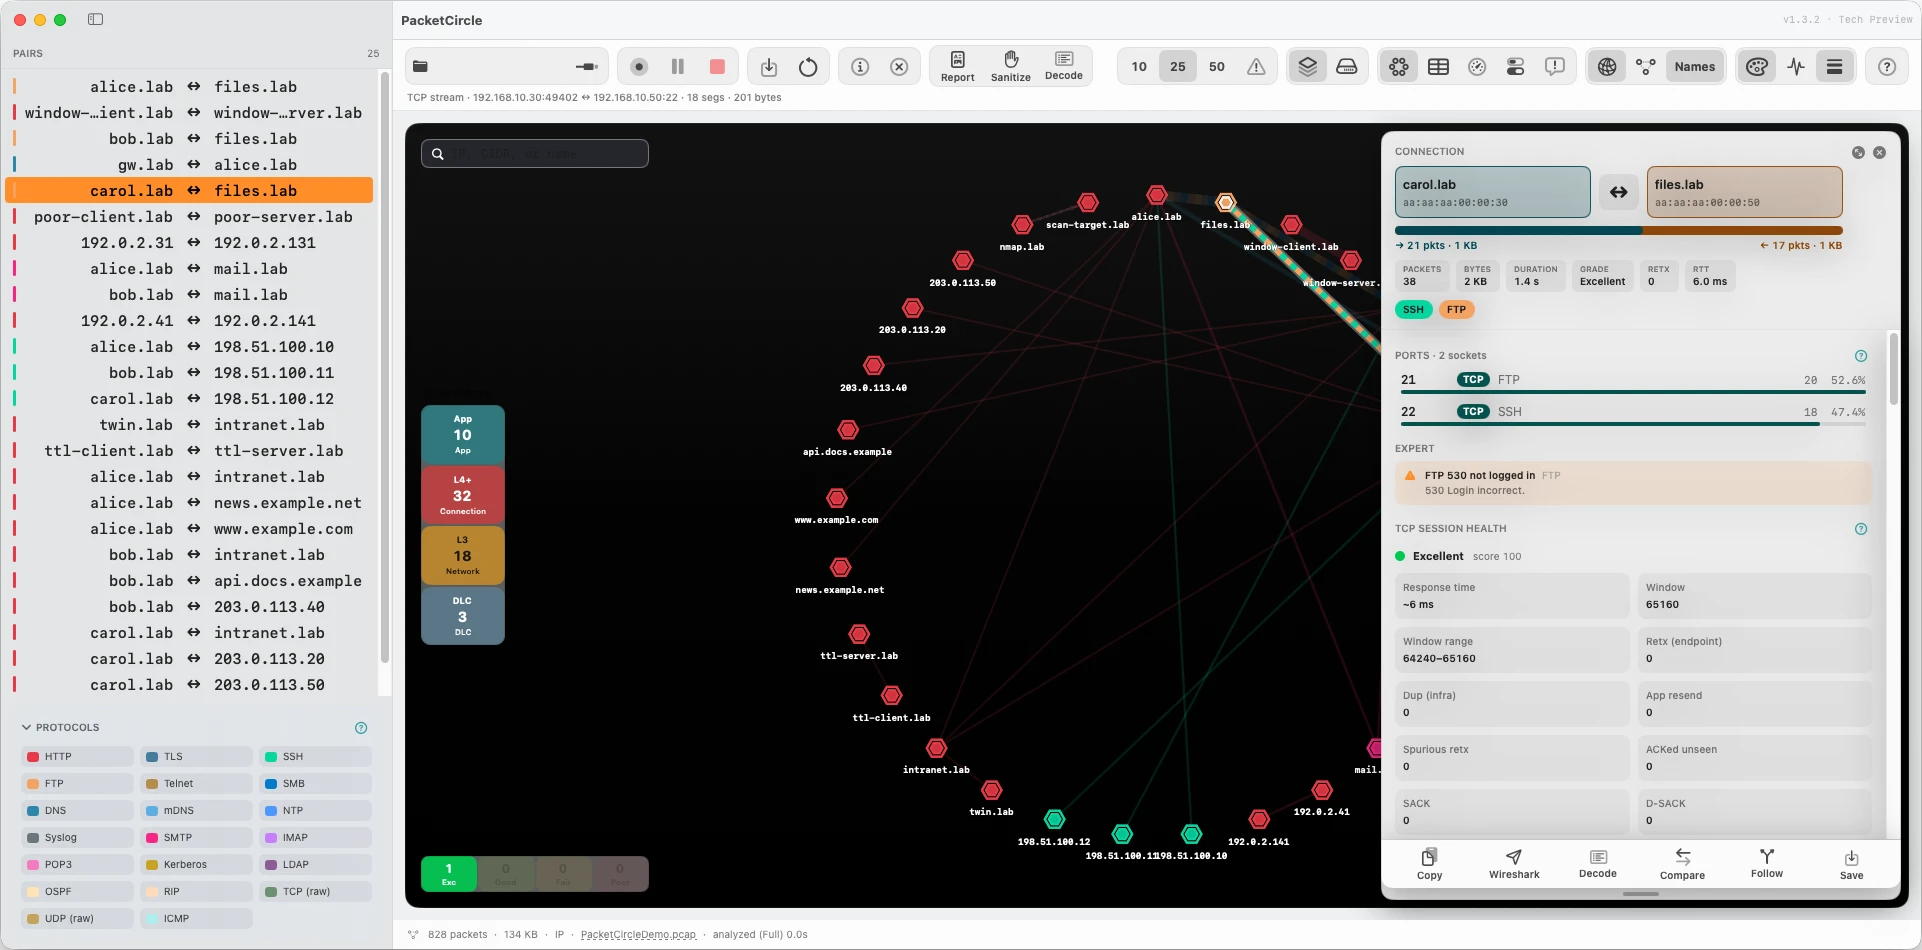
- Type expert and a group or message into the search bar to find Expert findings without leaving the Circle; the Help page for the Circle explains the syntax.
- Connection card (Mac): a conversation with TCP quality, several sockets or Expert findings now uses the full height of the Circle and follows the window size.
- Linux / Windows footer: while a capture is read, the frame counter is on the bottom bar and Stop sits at the right, as on the Mac.
- About and Help text on Linux and Windows no longer says “this Mac”.
PacketCircle 1.3.1 — Now on Linux, one Rust engine underneath, and an analyzer that is 13× faster
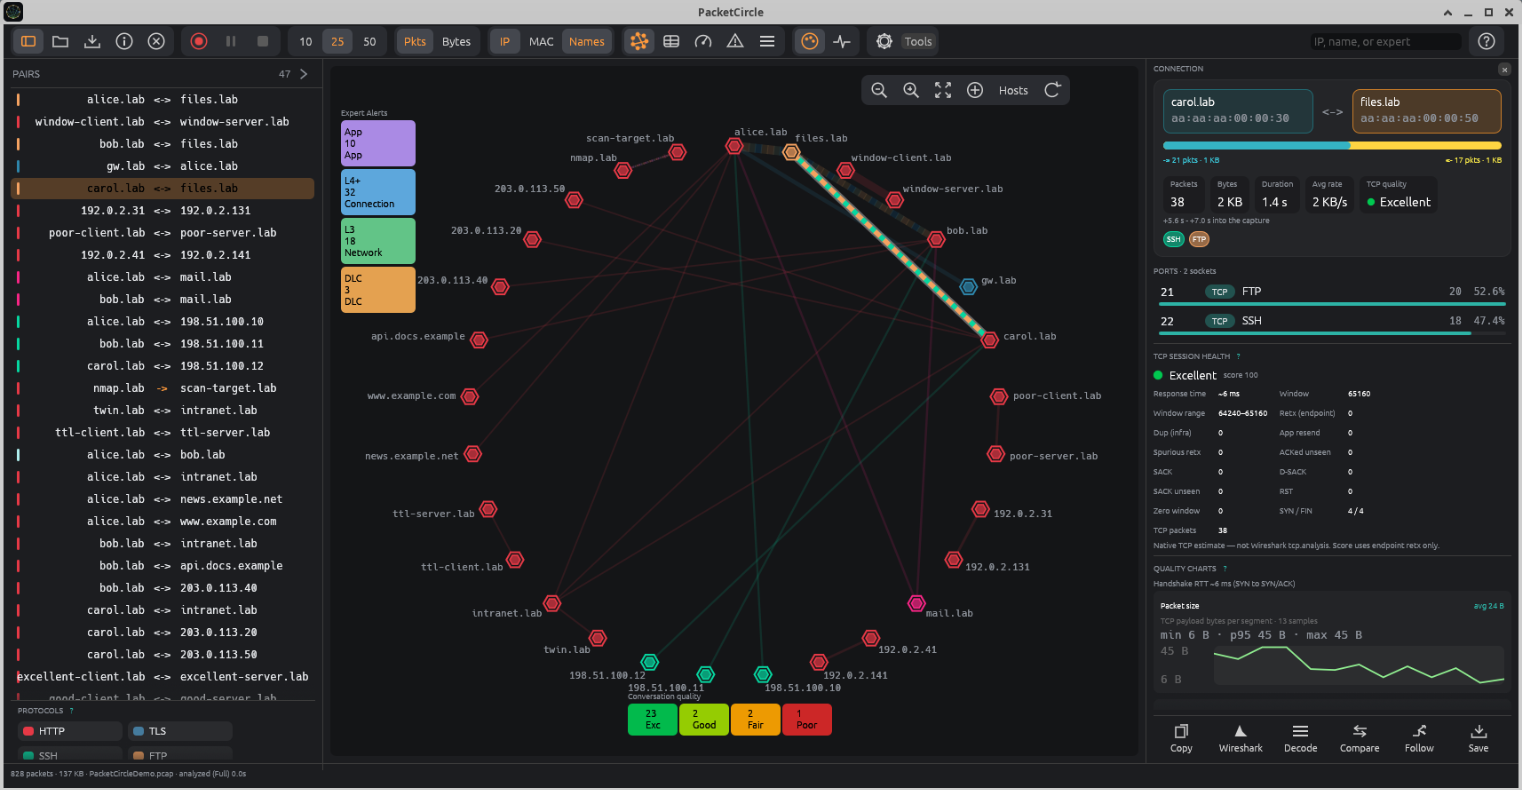
PacketCircle has been rebuilt around a single analysis core written in Rust. The Mac and iPhone/iPad apps keep their SwiftUI interface, and a new native desktop app brings the same Circle, Expert Alerts, Decode and reports to Linux — with Windows next on the same code. A 600 MB capture with 1.2 million frames that took 1 minute 7 seconds to analyze now takes 5 seconds. The Expert findings also gain a scan detector that names Nmap-style scans. Still native analysis, on device — not Wireshark.
iOS status: PacketCircle 1.3.1 for iPhone and iPad is now available on the App Store.
- Core and UI are now separate. Reading, dissection, analysis, TCP quality and Expert all live in one Rust core with no UI code in it.
- Mac and iOS: SwiftUI stays the interface. The Mac app already runs its analysis on the Rust core in this build (Apple silicon).
- Linux and Windows: one native app (Rust, egui) draws the same view models — it never re-implements the analysis. Linux ships today; Windows follows from the same code.
- The result: a fix or a new Expert rule is written once and shows up on every platform.
- Native desktop app for Ubuntu 24.04 (x86_64 download; the installer also supports aarch64); it also targets Fedora, Debian 13, Arch and openSUSE.
- Everything you know from the Mac: Circle with Hosts / Services / Infrastructure Map layouts, Conversation details with TCP session health and quality charts, Decode with display filter, Follow TCP Stream, Expert Alerts, Gauges with the quality timeline, Compare Conversations, Sanitize and PDF reports.
- Live capture from an interface and PCAP over IP; one-time capture permission with
setcap, no need to run as root. - Signed installer: a self-extracting
.runthat checks your machine, verifies the GPG signature and installs for you or for everyone (a.debis included too). It comes as one.zipdownload with all the installers (.run,.deb,.tar.gz), checksums, signatures and a short readme.
- 600 MB capture, 1.2 million frames: 1 min 7 s before, 5 s now. Moving the analysis from Swift to Rust was the key.
- A conversation index makes connection details open instantly even on huge captures, and Decode jumps straight to the selected conversation wherever it sits in the file.
- Captures of 200 MB or more ask for Light or Full analysis; progress shows conversations, applications and frames found so far, with a Stop button. The footer reports how long the analysis took.
- New header with endpoint blocks (name, address, MAC, port), stat chips, a direction split bar and protocol pills; ports show their share of traffic.
- Application messages are drawn as a two-lifeline sequence diagram; identical neighbours collapse to ×N.
- Copy capture filter gives a BPF for the pair, narrowed to
tcp portorudp portwhen a socket is selected.
- Jumbo / giant frames now count the bytes actually stored in the capture. A larger PCAP “original length” left by snaplen or Linux GRO/GSO is no longer a jumbo frame: a 1514-byte frame stays under the 1518 threshold. Decode still shows the claimed original length when it is larger.
- New Expert Alerts page (Mac) with Link, Network, Transport, Application and All tiles. Tiles include notes; the Circle chips still count warnings and errors only.
- Hide a finding for one conversation, or suppress the alert type — from the Expert tiles on Linux and the alert list on the Mac.
- Half-open SYN, service, FIN, Christmas-tree, NULL, ACK, UDP and User-Agent scans are raised as warnings on the connection band (L4+).
- An ARP sweep is raised on the network band (L3).
- Nmap is named when the time window and the volume match.
- The demo capture contains one Nmap SYN scan (ports 22, 80, 443, 8080) and one Christmas-tree scan (FIN+PSH+URG on ports 21, 23, 25, 110, 143) — open it and look at the Expert Alerts.
- Gauges are clickable: Hosts, Protocols and TCP health apply the matching Circle filter; problem conversations sit beside the quality timeline.
- Sanitize on save: Save and Save Session ask whether to scrub the capture first.
- Report logo: add your own PNG/JPEG to the PDF cover.
- Toolbar: Info always works (Capture details, or About when nothing is open), Help sits at the right, Close capture is a circled ×.
- Protocol legend folds away under the pairs list and remembers its state.
- PacketCircle Native stays free of charge and unlimited — no ads, no in-app purchases, no telemetry.
- It is not open source (yet). Everything is built with the GPL in mind, but after this complete re-architecture it is not published under GPL-2.0 today. I plan to release the sources as soon as I feel comfortable; if your organization wants to see them before that, just ask — there is no secret.
- The original PacketCircle Wireshark plugin is unchanged and remains open source (GPL-2.0).
PacketCircle 1.2.6 — Infrastructure Map on iPhone, and Expert findings that stay on topic
The Infrastructure Map comes to iPhone as a third Circle layout, built from the switching and routing protocols in your capture. Expert findings in Session details now follow the socket you are looking at, so an HTTP conversation no longer shows FTP or mail alerts from the same pair of hosts. Still native analysis, on device — not Wireshark.
- New third Circle layout: Hosts → Services → Map.
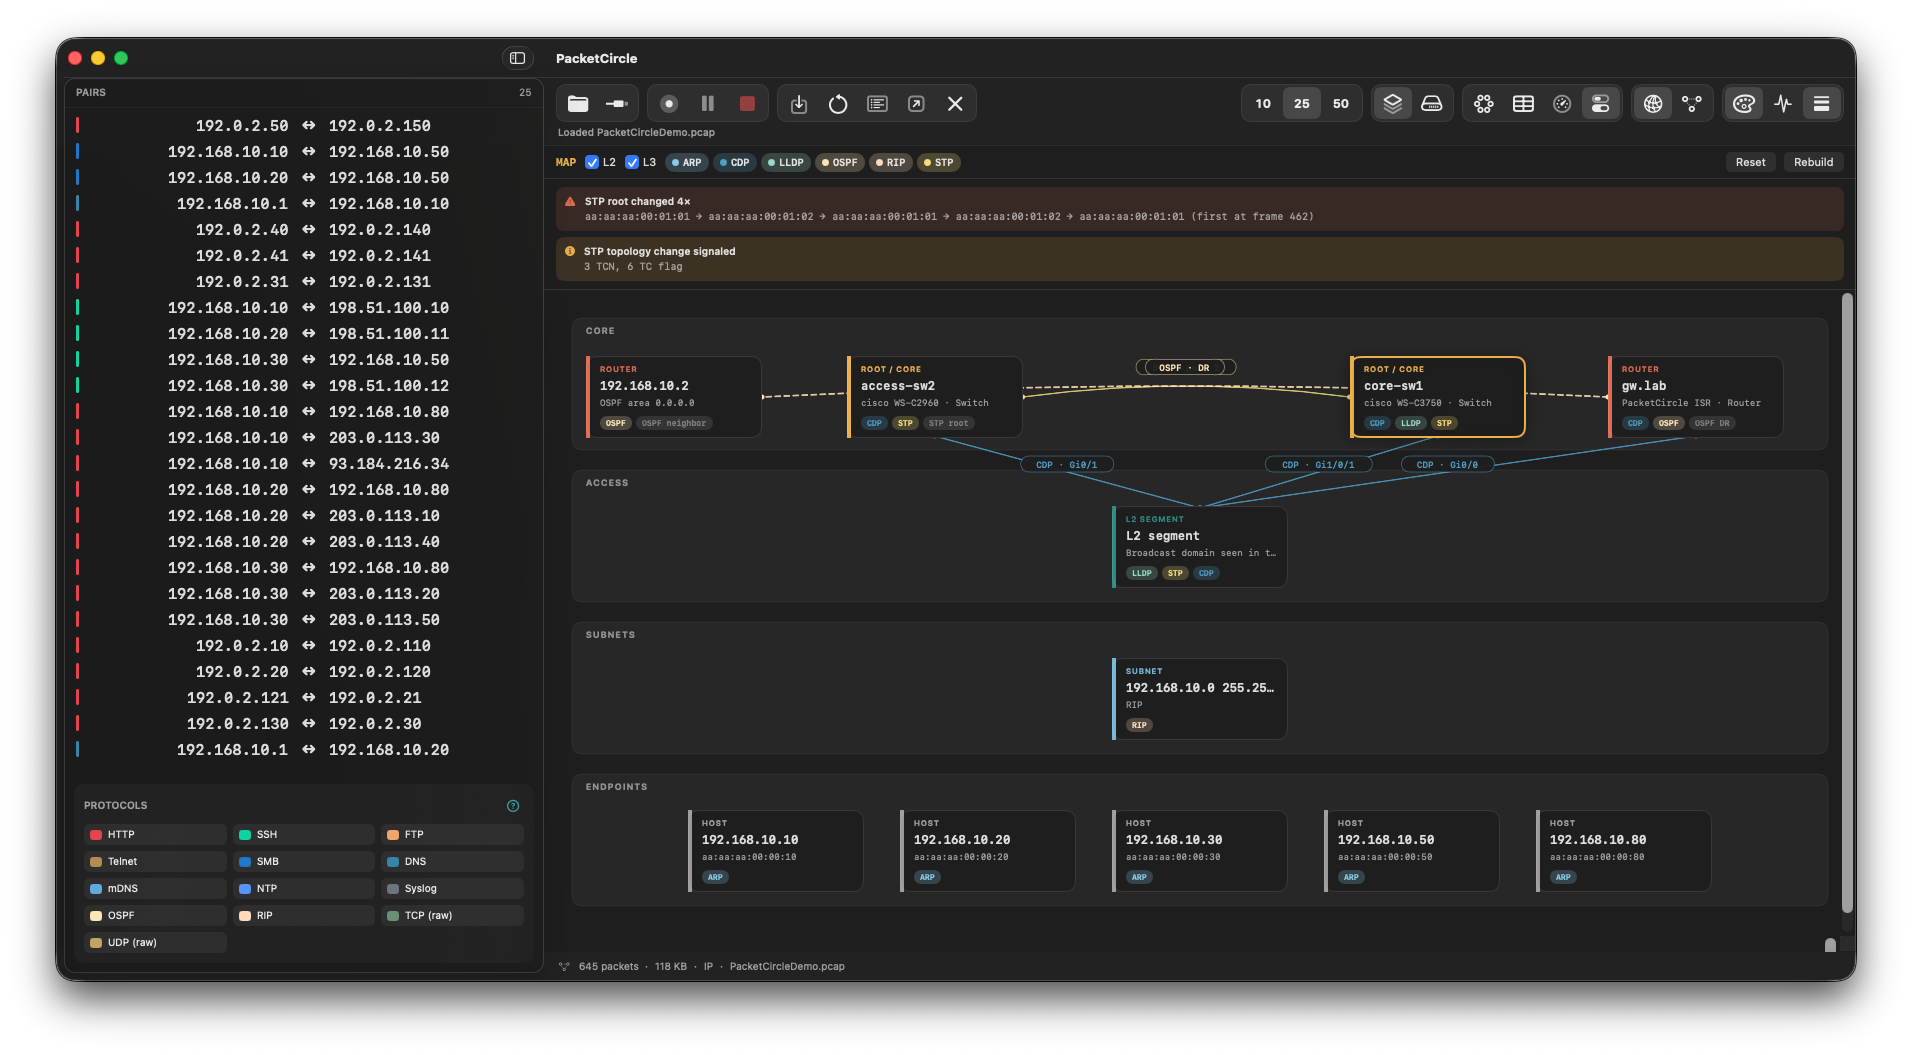
- Core / Distribution / Access drawing learned from STP, CDP, LLDP, OSPF, BGP, EIGRP, IS-IS, RIP and ARP in the capture — devices that never spoke in the trace are left out on purpose.
- Toggle L2 and L3 separately; STP root changes and topology-change signals appear as alerts above the map.
- Tap a switch or router to open its Session details.
- Don’t need it? Options → Circle → Show Infrastructure Map turns it off (Mac: Settings → General → Circle).
- Pick a socket (for example TCP 80) and the Expert list shows only that service’s findings, that socket’s TCP health, and host-wide network or link findings.
- A short note tells you when more findings sit on other sockets of the same conversation.
- New Other sockets list at the bottom of Session details: switch sockets in one tap, with a warning marker on the ones that have alerts. Whole conversation is one tap away.
- Circle (Mac Settings · iOS Options): show or hide the Expert Alerts strip, the Conversation quality bar, and the Map layout.
- Conversation details: show or hide Expert findings and TCP session quality panels. Services and decode always stay available.
- NetBIOS Name Service: queries, responses, name records and NBSTAT name tables — names also feed the host labels.
- NetBIOS Datagram and the Windows Browser protocol (
\\MAILSLOT\\BROWSEhost announcements, elections). - Separate labels for NetBIOS-NS, NetBIOS-DGM and NetBIOS-SSN (ports 137–139).
- Kerberos findings only on Kerberos traffic (ports 88 / 464) — no more false alarms on unrelated TCP streams.
- Jumbo / giant frame findings based on the real on-wire frame size.
- Same finding on two services of one conversation (for example HTTP 404 on :80 and :8080) is now listed per socket.
- Mac: right-click a TCP reset (or another alert) → Treat as normal for this conversation; manage exceptions in Settings → Expert.
- Fixed a crash when decoding certain Windows Browser election packets.
- Reset always returns the Circle to the IP view, even after filtering on link-layer (DLC) alerts.
- Show host names is on by default for new installs.
- Services layout line thickness better reflects traffic volume.
- Mac: recent captures on the start screen use one clean line each.
PacketCircle for iOS 1.2.5 — PCAP over IP, Sanitize, and PDF Reports arrive on iPhone
PacketCircle for iOS 1.2.5 just passed App Store review — the first iOS release to carry over three of the Mac/Wireshark-plugin Pro features: PCAP over IP remote capture (connect out to a sensor running pcapoverip or PolarProxy, the same convention Wireshark uses with -k -i TCP@host:port), on-device Sanitize (the PacketSanitizerPro payload-scrubbing modes, native on iPhone/iPad), and native PDF Report generation (the PacketReporterPro report set, built with the same pipeline as the Mac app). Still free, no ads, no telemetry, fully offline.
PacketCircle 1.2.4 — Capture/decode depth and iOS live-stream polish
More of the wire gets decoded natively, and remote live capture gets easier to reach and more honest when it breaks. Still native analysis, on device — not Wireshark.
- IGMP / MLD decode — group addresses, v1/v2/v3 queries and reports (source lists, INCLUDE/EXCLUDE), well-known multicast labels (SSDP, mDNS, all-systems).
- TLS on HTTP alt ports — HTTPS on 8080 / 80xx / 8888 is labeled TLS when the payload is a TLS record; plaintext HTTP on those ports stays HTTP.
- PCAP over IP (client) — connect to a remote classic-PCAP stream (TCP@host:57012), same idea as Wireshark -k -i TCP@host:port.
- Payload NetFlow / syslog — custom collector ports (e.g. UDP 515) classify from the datagram, not only IANA 2055/514.
- Richer mDNS — Bonjour service types, cache-flush / QU, additional A/AAAA.
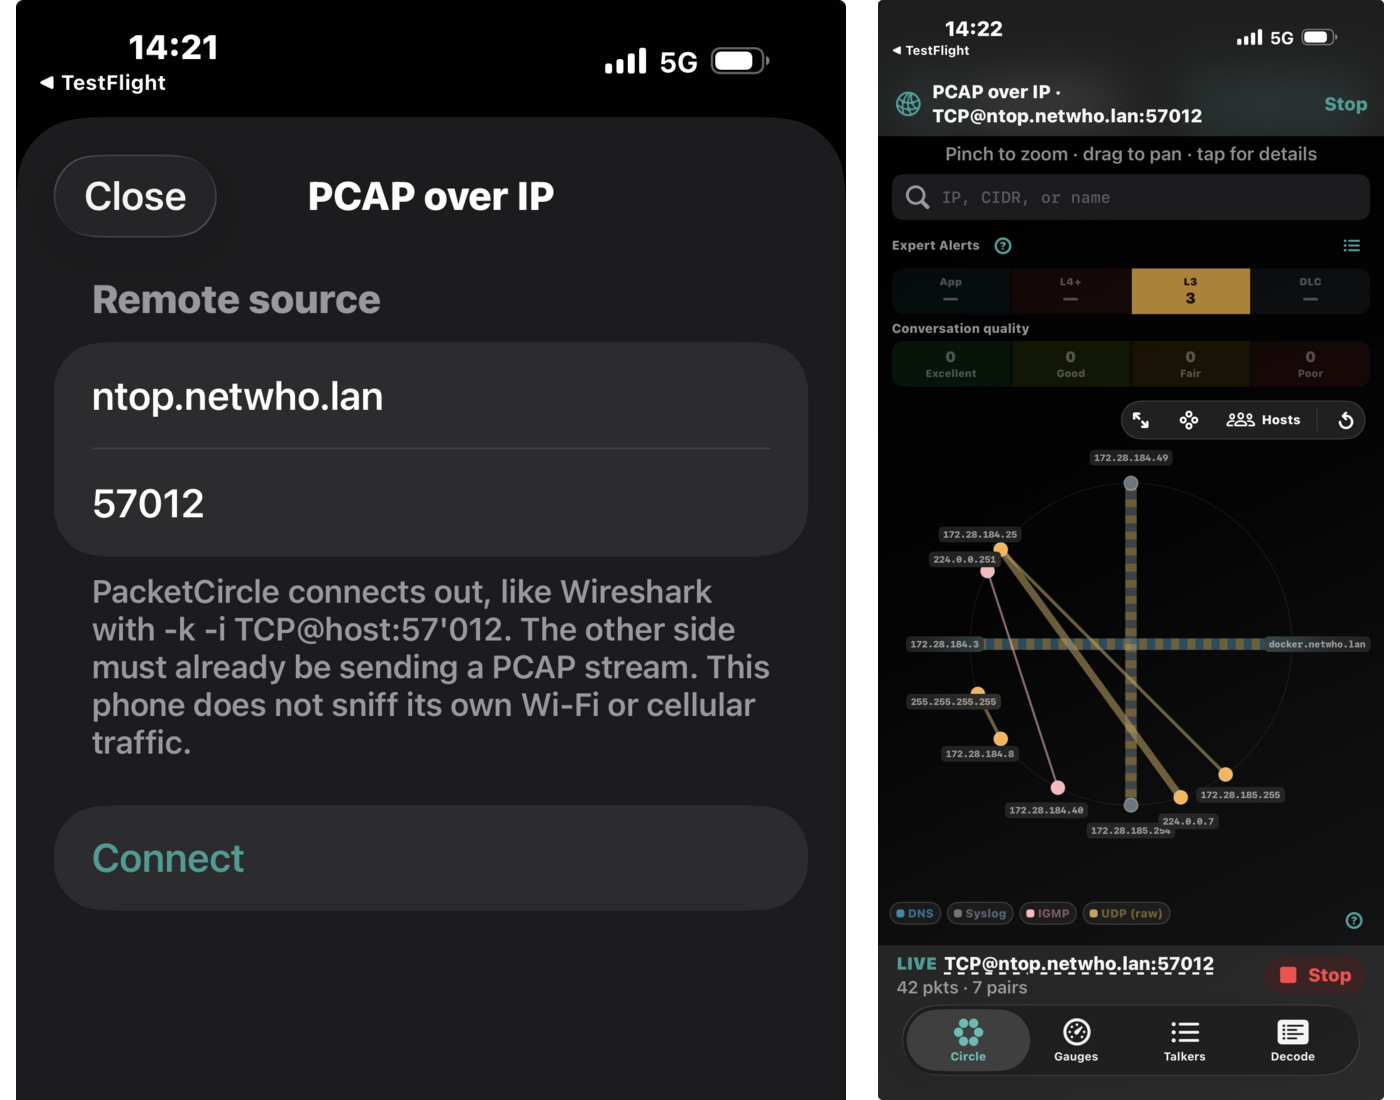
- Live PCAP-over-IP no longer re-analyzes the whole file every second or re-packs the Circle ring.
- iOS remote-connect failures no longer look like a Files import error; invalid host/port is shown in the sheet.
- Options → PCAP over IP waits for Options to dismiss before presenting the connect sheet.
PacketCircle 1.2.3 — Display filter, Expert Alerts, and tunable thresholds
Decode now has a Wireshark-style display filter beside search. Reports (Detailed and Field guide) include an Expert messages section built from the capture-wide expert modules. Settings → Expert exposes the thresholds that actually differ from network to network. Still native analysis, on device — not Wireshark.
- Display filter next to text/hex search (Mac window and iPhone tab).
- Familiar syntax: tcp, tcp.port == 80, ip.addr == 10.0.0.1, http and tcp.flags.syn, contains, and/or/not.
- Autocomplete from PacketCircle’s catalog only. Unknown names (ospf, wlan, tcp.stream) turn the filter red and do not silently match.
- tcp.analysis.* for experts I raise myself: retransmission, spurious retransmission, ACKed unseen, zero window, duplicate ACK.
- ARP request storm (who-has burst per second) and ARP unanswered (retried who-has with no reply in the file).
- Experts on the Circle toolbar (after Top 10/25/50): show conversations with warn/error alerts, not only the busiest (cap 250). Solo an Expert Alerts band first to restrict the layer.
- Duplicate-IP, local routing / hairpin, ICMP, HTTP/TLS/apps, and TCP quality experts as before.
- New Expert messages section (Detailed + Field guide): type, description, counters, sample nodes/pairs.
- Per type: what triggered it, typical use, and when the finding can be informational — present in the capture without proving a connectivity or performance outage (SPAN duplicates, traceroute TTL=1, jumbo frames, one-sided unanswered ARP, HTTP 404, encrypted TLS alerts, and similar).
Sliders for thresholds that vary by LAN:
- ARP storm warning / error (who-has per second)
- Unanswered ARP retry count
- Giant-frame size (raise this on jumbo/storage fabrics)
- Endpoint retransmit % and zero-window count
ARP sliders apply immediately to Expert Alerts and the report. Giant-frame size applies the next time the capture is analyzed.
- ICMPv6 Neighbor Solicitation no longer shows as a UUID-looking source to solicited-node multicast; DAD self-pairs are omitted.
- IP communication-matrix legend uses the same volume coloring as the chords (teal → red).
- Recent captures and drag-and-drop open on Mac.
PacketCircle 1.2.2 — Wireshark-style display filter in Decode
Decode now has a display filter next to the existing text/hex search, on the Mac window and the iPhone tab. It takes the Wireshark syntax I already know for the protocols and fields PacketCircle actually decodes, with autocomplete as I type: tcp, tcp.port == 80, ip.addr == 10.0.0.1, http and tcp.flags.syn, chained with contains, and/or/not. Autocomplete only offers names from PacketCircle’s own catalog, not Wireshark’s full field tree — unsupported names like ospf, wlan, or tcp.stream turn the filter red and leave the packet list untouched instead of silently matching nothing. The tcp.analysis.* terms — retransmission, spurious retransmission, ACKed unseen, zero window, duplicate ACK — come from PacketCircle’s own per-packet experts, not a port of Wireshark’s analysis engine, so early-retransmission and TCP SACK sequence behaviour reflects how PacketCircle itself decodes the stream, not how Wireshark would.
PacketCircle for macOS 1.2.1 — Tech Preview
Since 1.1.0, the Mac build moves from “circle + decode + TCP health” to a fuller triage workflow: an OSI-layered Expert Alerts strip on the Circle (App → L4+ → L3 → DLC) that you can filter, browse, and suppress noisy alert types; richer Decode with per-frame Expert Info and honest cleartext-vs-encrypted TLS alerts; the 1.2.0 Pro tools shell with native Sanitize Capture and PDF Generate Report; side-by-side Compare Conversations; and a topology Map with STP context.
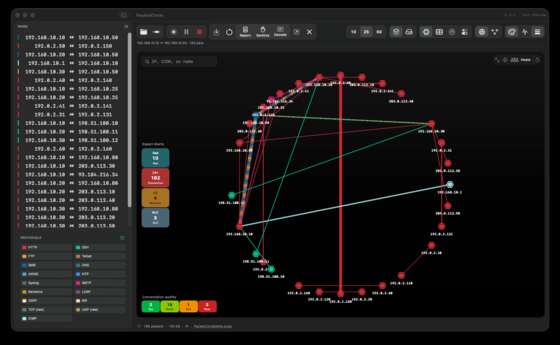
PacketCircle for iOS is live on the App Store
PacketCircle for iPhone (1.1.0) just passed App Store review — free, no ads, no in-app purchases, no telemetry, and fully offline. It’s the mobile counterpart to the Wireshark plugin: load a PCAP/PCAPNG and get the same circle-first view of who’s talking to whom, plus native TCP session health, Follow TCP Stream, and a built-in demo capture to try it without a file. Full write-up below covers the why, the App Store constraints (no live capture, no GPL code shipped), and the complete feature list.
Sneak preview: the macOS Infrastructure View
The macOS build (private Tech Preview) is picking up analysis modules the iOS/Wireshark-plugin side doesn’t have yet. The newest one is an Infrastructure View that reconstructs your routing/switching topology directly from control-plane chatter in the capture — CDP, LLDP, STP, OSPF, ARP, RIP and friends — and lays it out as Core / Access / Subnets / Endpoints, complete with STP root-change and topology-change alerts. No config access, no SNMP: just what the wire already told you. Still shaping up, but early enough to share.