- About
- Get the game
- Quick start
- Controls
- Modes & skill
- Your tools
- Strategy
- The tickets
- Pet networks
- What is simulated
- FAQ
About
Ping the Networker is a data-center jump-and-run for people who know what STP stands for, and for people who want to find out. You play Ping, the hall’s network engineer. Each level is a trouble ticket: some client cannot reach some server. You find out why, fix the configuration and press Send. The packets travel through the simulated network hop by hop and the game tells you where and why they drop.
It is free, runs in the browser and needs no account. On iPhone and iPad there is a native app that works offline. Scores and optional 3-letter initials go to a shared high-score table on netwho.ch.
Get the game
- Browser: any current desktop browser; keyboard recommended. On touch devices the game shows on-screen buttons; use landscape.
- iPhone and iPad: landscape app, free, works offline, no account.
- Pet networks are part of the browser version only.
Quick start
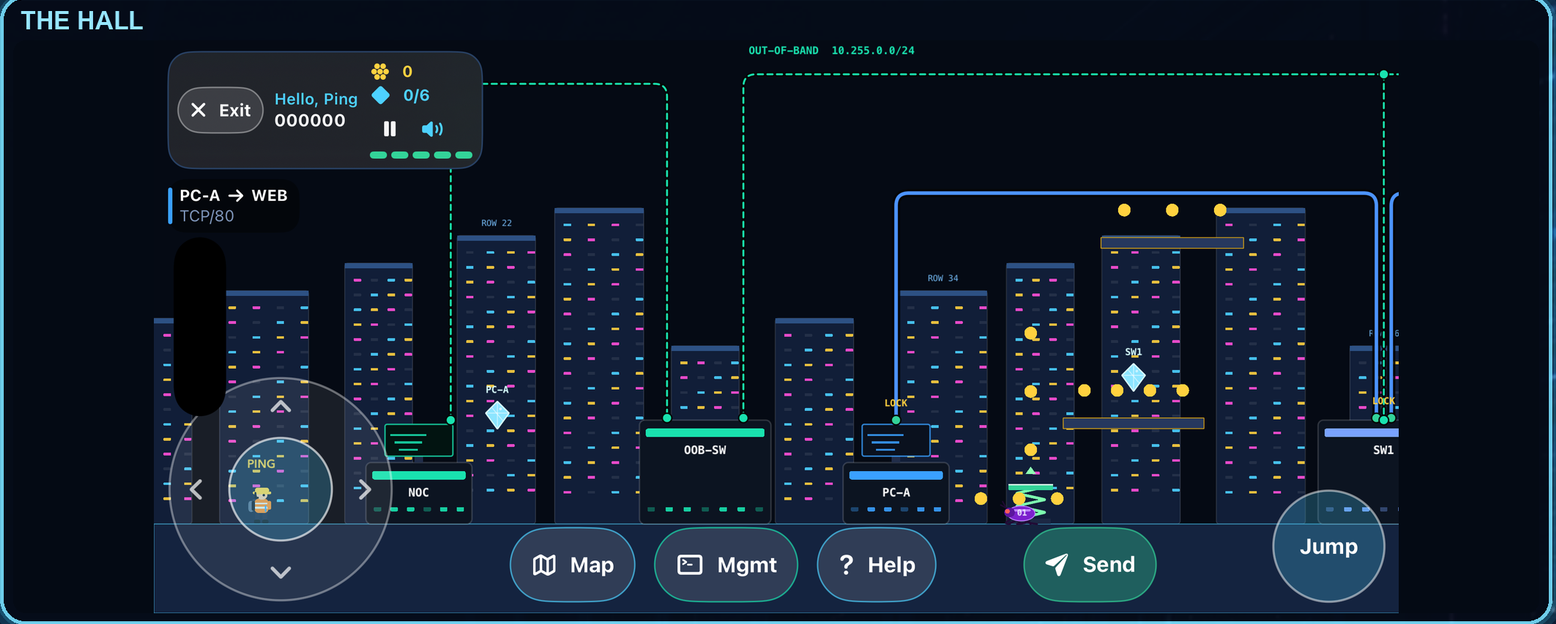
- Read the ticket in the bottom bar. The packet colour is the source client, the server colour the destination, and the label says the protocol and port, for example
PC-A → WEB TCP/80. - Run the hall and collect the diamond of every device you want to configure. Until you do, the device is locked, including over SSH.
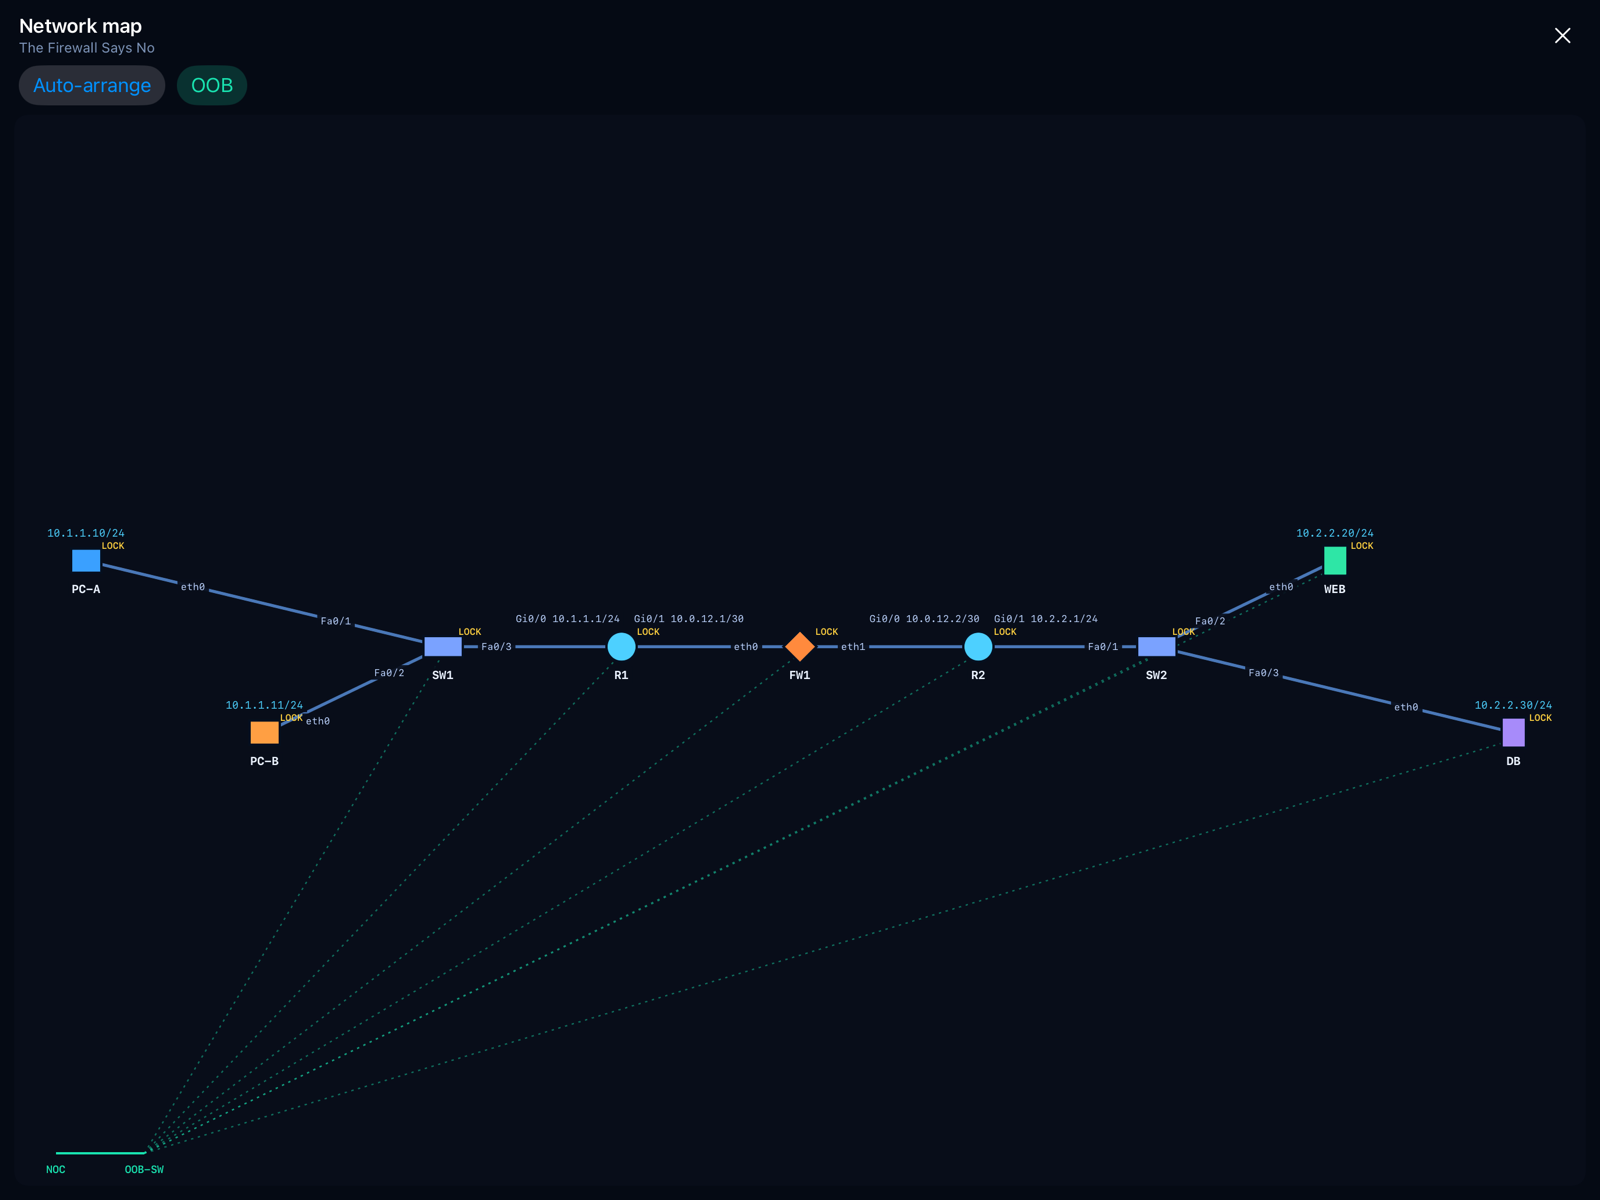
- Look at the network map (Tab). It shows every address, mask, port and link and the path the packet has to take.
- Press Send (G) once on the broken network. The failure message and the ❗ marker show you the first place where the packet died.
- Fix that device: press E next to it for its console, or T for the SSH terminal.
- Send again. Fixing one fault often reveals the next. A ticket is solved when the packet arrives and the answer comes back (or, for a hostile ticket, when it is blocked).
Controls
| Key | Action |
|---|---|
| ← → or A D | Run |
| Space, ↑ or W | Jump; press again in mid-air for a double jump |
| E | Open the console of the nearest device (needs its diamond). At the NOC desk this is the management console |
| T | Management console: SSH over the out-of-band network |
| G or Enter | Send the packets |
| Tab | Network map. Drag devices, hover for details, Auto-arrange resets |
| ↓ + jump on a green pad | Spring pad: super-jump to the high ledges (landing on it from above works too) |
| F / ⏩ button | Packet speed ×2 → ×4 → skip to the results (the SEND button turns into ⏩ while packets fly; holding it for 2 s also skips) |
| C | Open the capture analyzer after a send |
| H | Help, three levels (see below) |
| M | Mute |
| Esc | Pause menu |
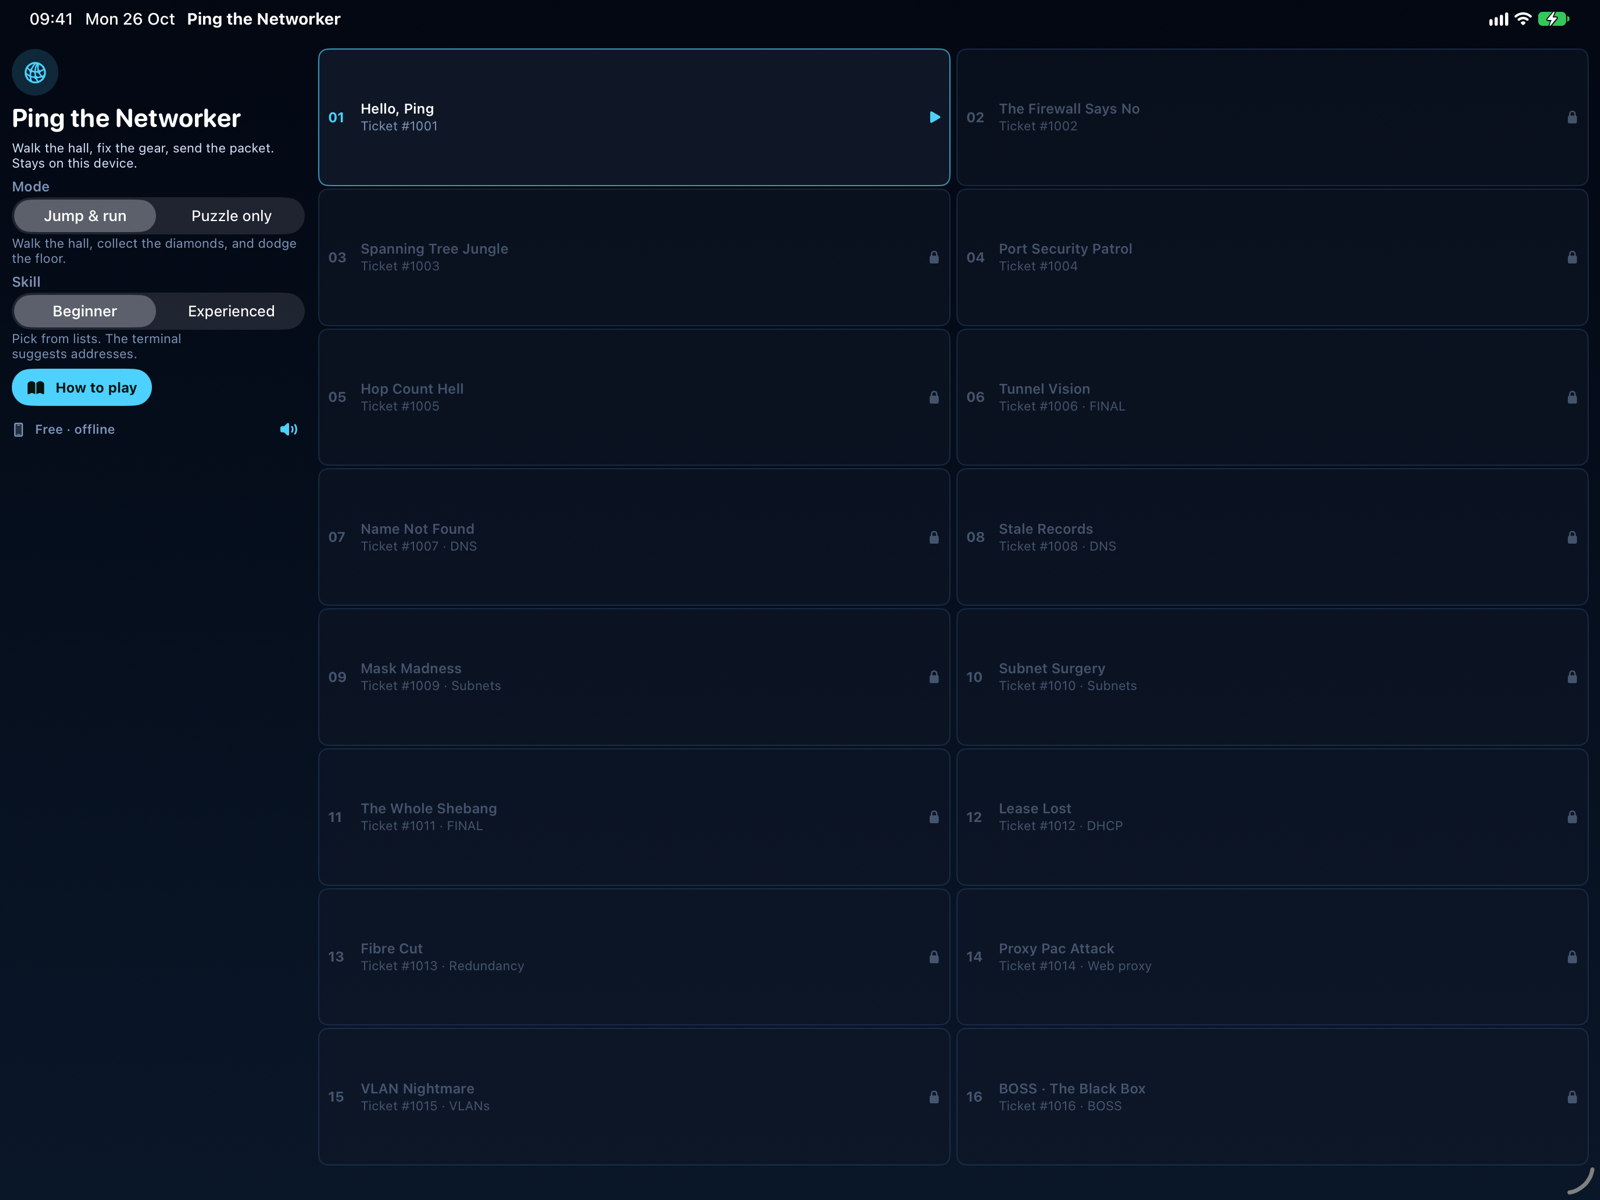
The title screen also has a How to play button with the same information as a tabbed manual.
Modes and skill levels
Mode
- Jump & run (default): collect diamonds, dodge pits, bugs and lasers, ride moving platforms and fans, use spring pads to reach high ledges. Each level has its own obstacles. Diamonds are worth +25 each, and collecting all of them in a level adds a +100 bonus.
- Puzzle only: no obstacles and nothing locked. Press D to pick a device and Ping walks there. Puzzle runs are not listed in the high scores.
- 🎓 Training: for people new to networking. A teacher guides you through all 16 tickets (see Training mode below). No running, no pet networks, no scores, always pick-lists. All lessons are unlocked.
Skill
- Beginner: routes, addresses and masks are picked from lists, and the terminal suggests values with Tab and ?.
- Experienced: you type everything yourself (
10.2.2.0/24and the next hop, masks as/24or255.255.255.0, gateways, DNS servers). The terminal only completes keywords. You earn +25 % of the level score.
Your tools
Device consoles
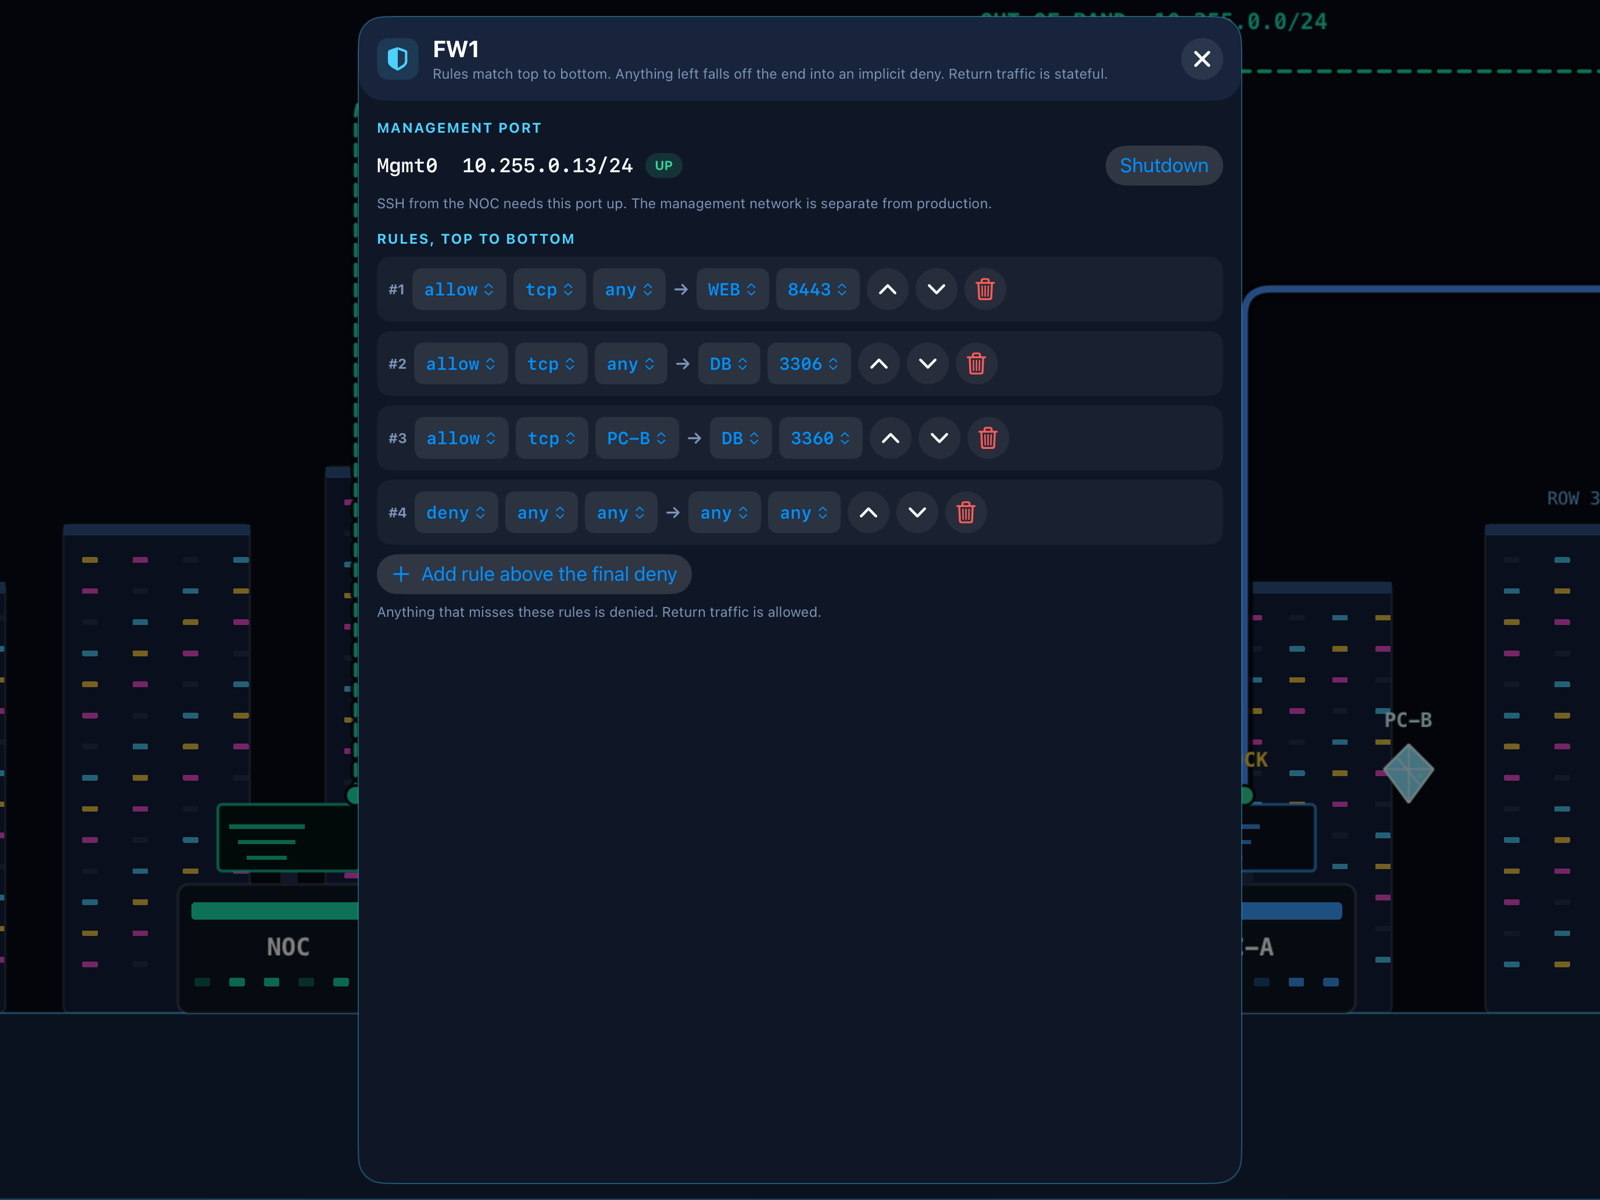
Walk up to a device and press E. Routers have interface addresses, static routes and an MSS clamp. Switches have RSTP, priority, port shutdown, port security, VLANs and trunks. Firewalls have an ordered rule list. Servers have address, gateway, DNS zones and DHCP scopes. Workstations are configured at the desk.
The SSH terminal
Every switch, router, firewall and server has a Mgmt0 port on a separate out-of-band network (10.255.0.0/24), drawn as dotted teal cabling. Press T, then type ssh R1. The CLI is small and Cisco-like: modes (configure terminal, interface …), unique abbreviations (sh ip ro), Tab completion, ? context help, history, do show …, ping, traceroute, show running-config. The GUI consoles and the terminal share the same state, so use whichever you prefer. If you shut down a device’s Mgmt0 port, you can no longer SSH to it.
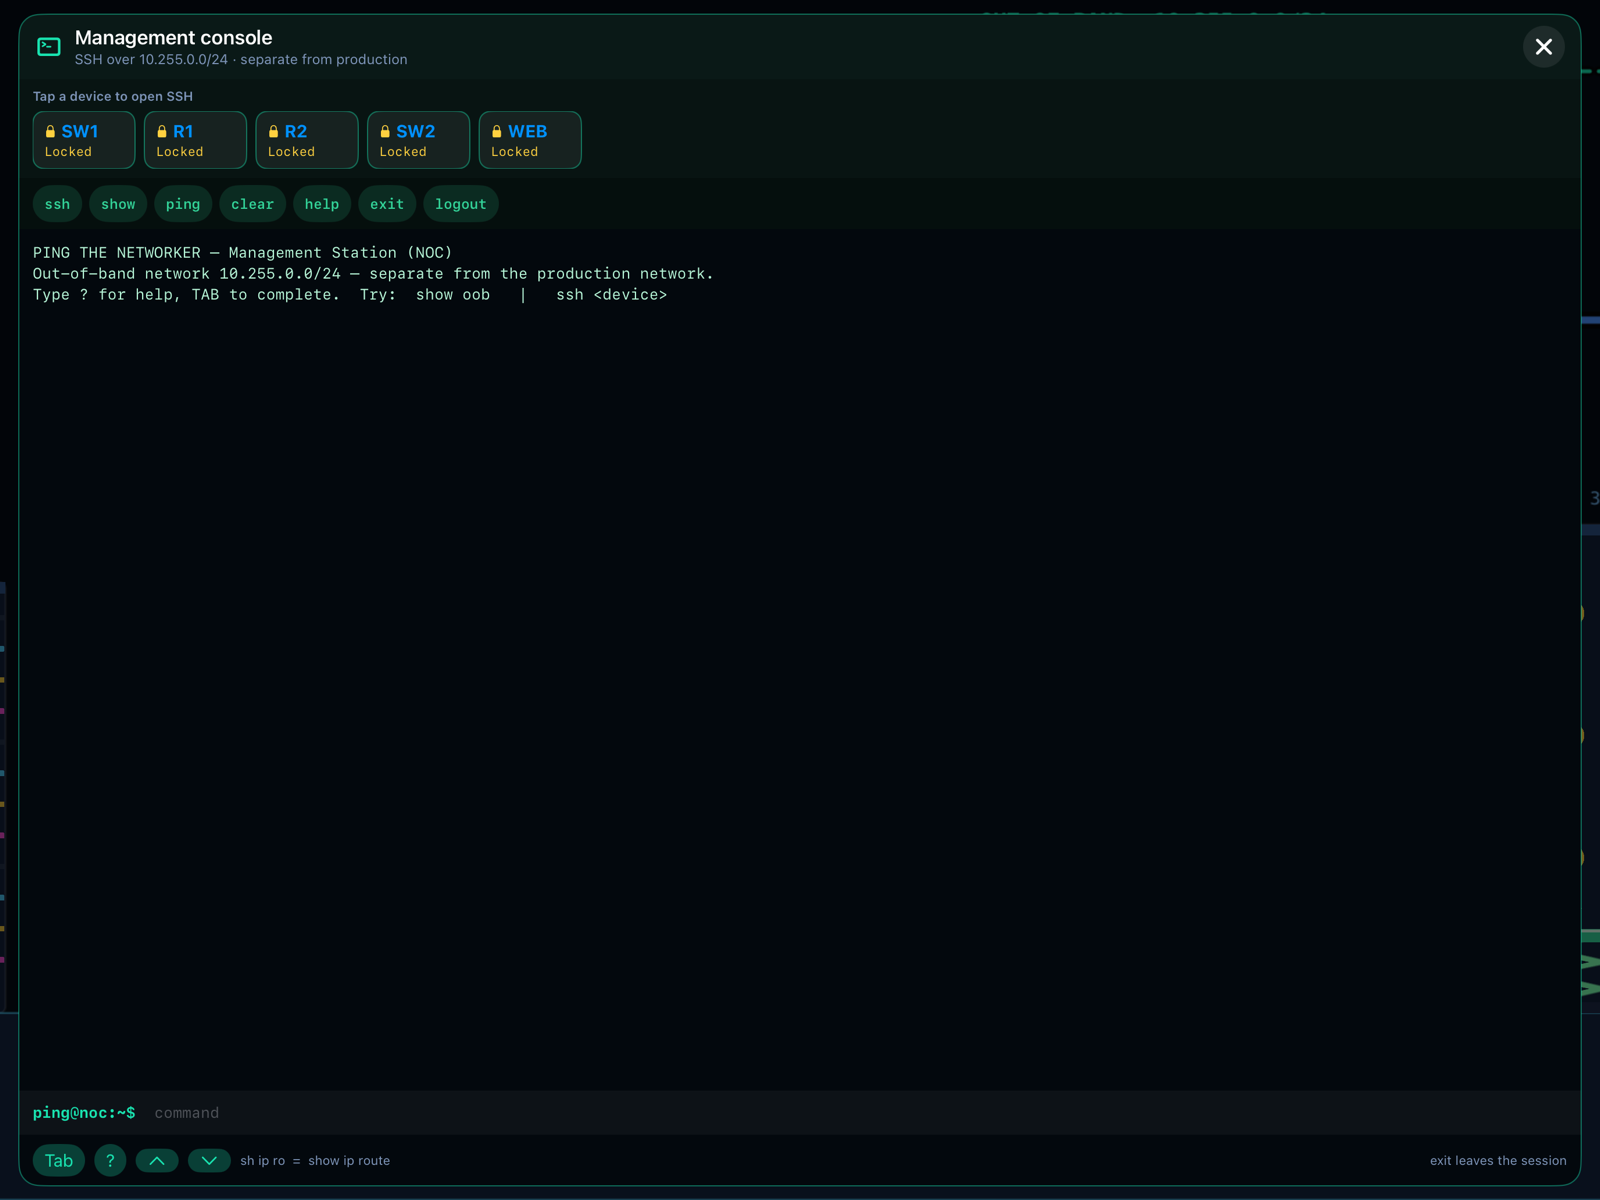
ssh and a device name to log in over the out-of-band network.The network map
Press Tab. Every device has its own box, every IP address, port and network ID sits on a label plate, and hovering a device shows everything about it. You can drag devices to arrange them and toggle the out-of-band layer. A red ✕ marks a cut fibre. Click a device on the map to beam Ping right next to it — no more running across the hall (in Jump & run mode; the device still needs its diamond to unlock, and you press E to open it).
The capture analyzer
After every send, press C to open a Wireshark-style analyzer. Pick a capture point (any device on the path), filter with display filters and read the packet list, the decoded protocol tree, a real hex dump with valid checksums and the Expert info tab. Useful filters: ip.addr == …, tcp, dns, icmp, arp, tcp.port == 443, tcp.analysis.retransmission, !arp. The frames include ARP, DNS over UDP and TCP, TCP handshakes, TLS Client Hello, ICMP errors with quoted packets, and retransmissions.
Getting help
Press H for three levels: a nudge, a diagnosis, the exact fix. The game asks “Are you sure?” first, because a session that used help is not listed in the high-score table and the level is recorded as “with help”. The failure messages, the map, the capture analyzer and the Beginner skill level are always available and cost nothing.
Strategy and tips
Think like a packet
- Follow the path, both ways. The request has to arrive and the answer has to find its way back. A missing return route is the most common second fault.
- Work from the source outward. The first ❗ is where the packet died. Fix it, send again, and move on to the next one.
- Read the drop reason. “No route”, “TTL exceeded”, “denied by firewall” and “no ARP reply” each point to a different layer.
- Check the basics on the host: IP, mask, gateway and DNS. A /16 where a /24 belongs, or a gateway outside the subnet, cause “routing problems” that are not routing problems.
Routing and switching
- Longest prefix wins. A more specific route silently beats your default route.
- A routing loop burns the TTL. Look for two routers pointing at each other.
- Switch triangles need RSTP. With it off you get a broadcast storm; with it on, one link blocks by design, so do not “fix” the blocking port.
- Port security with a hub behind it will err-disable the port. Find the rogue laptop.
- VLANs: a different VLAN is a different broadcast domain. Check the access VLAN of the port, the allowed VLANs on the trunk and the router leg.
Firewalls, DNS and the rest
- Rules match top to bottom, and anything unmatched is denied. Look for typos in the port first.
- Least privilege. An
allow anyrule makes the ticket pass but lets the hostile packet through too. Hostile tickets must be blocked. Watch for “temporary” lazy rules at the top of the list. - DNS has two failure modes: the PC points at the wrong resolver, or the record on the server is stale or missing.
- Over IPsec, remember the MTU: the DF bit, the TCP MSS clamp and path-MTU black holes when ICMP is filtered.
- For DHCP, check the relay (
ip helper-address), the scope’s gateway, the range against static addresses, and whether a rogue server sits on an untrusted port.
Scoring
- Play Experienced for the +25 % bonus.
- Collect all diamonds for the +100 bonus. The pause-menu “Unlock all devices” skips it.
- Do not use H if you want to be listed.
- Packet speed (the ⏩ button or F; a third tap or a 2-second hold skips straight to the results; or hold Space while packets fly) saves time and does not cost points.
Boss level tip: “The Black Box” has no markers, no ICMP messages and no animation. Use the capture analyzer at several points on the path and compare what you see at each one.
The tickets (16 + Pack 2)
| # | Ticket | What breaks |
|---|---|---|
| 1 | Hello, Ping | Missing static routes, and the missing return route |
| 2 | The Firewall Says No | Wrong ports in the rules, least privilege |
| 3 | Spanning Tree Jungle | STP off on a triangle, a shut-down port |
| 4 | Port Security Patrol | A hub behind a secured port, a rogue laptop |
| 5 | Hop Count Hell | Routing loop, TTL budget, longest-prefix match |
| 6 | Tunnel Vision | Routes, firewall, MTU and return path in one IPsec setup |
| 7 | Name Not Found | Wrong or missing DNS server on the PCs |
| 8 | Stale Records | Stale and missing A records on the DNS server |
| 9 | Mask Madness | Too-wide mask, dead gateway, gateway outside the subnet |
| 10 | Subnet Surgery | Duplicate IP, a /30 router interface, a server with a bad gateway |
| 11 | The Whole Shebang | DNS across an IPsec tunnel, masks, firewall, MTU and return path |
| 12 | Lease Lost | DHCP: missing relay, wrong gateway in the scope, range collision, rogue DHCP server |
| 13 | Fibre Cut | Redundancy: forward and return routes must use the backup path |
| 14 | Proxy Pac Attack | Web proxy: PAC URL, wrong proxy port, a URL-filter false positive |
| 15 | VLAN Nightmare | Wrong access VLAN, a trunk that does not allow a VLAN, a guest in the staff VLAN |
| 16 | BOSS · The Black Box | Blind mode with seven stacked faults. Find them with captures |
| Pack 2 · Beyond the Wire (16 tickets, opens after ticket 6; tabs on the title screen) | ||
| 2.1 | Clock Strikes Twelve | Kerberos clock skew: set an NTP server on the PC and let udp/123 through the firewall |
| 2.2 | Don’t Use the IP | A mapped drive by IP address falls back to NTLM and is refused: use the server name, and fix a stale DNS record |
| 2.3 | The RPC Lost Its Way | Domain join needs ports 88, 389, 135, 445 and the dynamic RPC range, for one PC only |
| 2.4 | Access Denied, Which One? | Three users, one error: locked account, missing group, wrong share name. The SMB status tells them apart |
| 2.5 | Radius Down | 802.1X: the only RADIUS server is down. Add the backup server and open its firewall path |
| 2.6 | The Secret Handshake | RADIUS stays silent: unknown NAS address and a wrong shared secret |
| 2.7 | Only the Printers Fail | MAC authentication bypass: switch MAB on, list the MAC addresses, put printers in VLAN 30 |
| 2.8 | One Bar of Misery | Wi-Fi signal too weak: read RSSI and SNR, raise the transmit power |
| 2.9 | Channel Soup | Three access points on one channel: 20 MHz width and channels 1, 6, 11 |
| 2.10 | Band Aid | 2.4 GHz radio off, DFS channel on 5 GHz, band steering missing |
| 2.11 | Parking Lot Wi-Fi | Guest handshake visible from the car park: WPS off, WPA3, less power. A hidden SSID does not help |
| 2.12 | Evil Twin | A rogue access point with our SSID: contain it, use 802.1X and protected management frames |
| 2.13 | The Chatbot Knows Too Much | Prompt injection leaks HR data: least-privilege firewall rule for the bot |
| 2.14 | Token Flood | LLM gateway: API-key authentication and a rate limit per client |
| 2.15 | The Mystery Router | Shadow IT: rogue DHCP router and a hidden NAS. DHCP snooping and a shut port |
| 2.16 | BOSS · Everything Is Connected | Blind boss: clock skew, RADIUS failover, evil twin and a public AI chat, all at once |
Training mode (browser)
Training is a third mode for everyone who has never configured a router. Choose Training under Mode on the title screen and press Start training. The network is shown as a diagram, and a teacher panel on the right guides you through one lesson per ticket.
How a lesson works
- Meet the network. The ticket, the diagram, and short know-how cards you can open.
- Send. The first packet is meant to fail. The teacher shows where it was dropped and what the message means.
- Understand. What the failing device is for and what has to change on it.
- Fix, step by step. The Take me to button opens the device next to the panel. The exact field or button is highlighted, and where it helps, the matching CLI commands are listed. A pager walks you through each step and you can jump back.
- Send again. If a different problem remains, the teacher moves on to it. When the packet arrives you see what you fixed and what you learned, and the lesson is marked done.
Good to know
- The teacher uses the same diagnosis engine as the help levels, so the guidance follows what you actually changed. On the blind boss ticket the culprit stays hidden until you ask for help.
- Click a device in the diagram to open it, hover for its details. The map (M), capture analyzer (C) and terminal (T) work as usual.
- Every ticket starts with a note that the animation is a learning simulation: some details are simplified on purpose. A real TCP connection, for example, starts with a three-way handshake (SYN, SYN/ACK, ACK), while the game sends a single flow and shows where it stops.
- Training runs are not scored and do not appear in the high scores. Completed lessons are remembered in your browser.
Pet networks (browser)
Press P on the title screen. There are four networks of rising size: Garage Lab, Branch Office, Campus and Enterprise. Only the segment IDs are known; everything else is chosen from pull-downs. Each run generates a random scenario in one of two flavours:
- Build: a factory-blank network that you design.
- Repair: a running network that broke overnight, with two to four injected faults such as a lost route, a wrong next hop, a shut port, STP off, a wrong firewall port, a duplicate IP or a fibre cut.
You get one to three communications to make work, sometimes with a hostile one that must be blocked. There is an optional time limit (3, 5, 8 or 12 minutes), and a scenario code lets you replay a scenario.
What is simulated
| Area | What the engine models |
|---|---|
| Routing | Connected and static routes, longest-prefix match, default route, TTL, loops, return path |
| Switching | RSTP root election and blocking, port shutdown, port security with err-disable, broadcast storms, hubs, VLANs and trunks |
| Firewall | Ordered rules, implicit deny, stateful return traffic, hostile tickets that must be blocked |
| DNS | Resolvers per host, editable zones, missing, stale or unreachable servers, DNS over TCP |
| Hosts | IP, mask, gateway and DNS; duplicate IPs, too-wide masks and gateways outside the subnet are detected |
| VPN / MTU | IPsec tunnel MTU, DF bit, TCP MSS clamp, fragmentation, PMTUD black holes |
| DHCP | Relays, scopes, exclusions, DHCP snooping and trusted ports |
| Web proxy | PAC files, manual proxy settings, URL-filter categories and exceptions |
| Terminal | Cisco-style console on routers, switches and firewalls: enable, show commands (routes, MAC and ARP tables, CDP, VLANs, spanning tree, port security), configuration modes, pipes and ? help. Real commands that are not simulated are listed with a remark. |
FAQ
What is Pack 2
Pack 2, Beyond the Wire, adds Windows and Kerberos tickets. It opens once you have solved ticket 6 and has its own tab, progress and Training lessons. Firewall rules in it accept port ranges, for example range 49152 65535 in the terminal. It has 16 tickets: Windows and Kerberos (2.1–2.4), RADIUS and 802.1X (2.5–2.7), Wi-Fi quality and security (2.8–2.12), AI chatbots and gateways (2.13–2.14), shadow IT (2.15) and a final boss (2.16). The terminal knows the new devices too, for example show aaa servers, show ap rogue and llm rate 120.
Can I start over
Yes. On the title screen, change your initials or choose reset progress. It asks for confirmation and clears scores, unlocked tickets and Training progress in this browser only.
What are the arcade toys beyond ziplines and pipes
Four more optional toys, all announced before they can hurt and each costing at most one SLA nine: a broadcast storm (a wave of frames rolls along the floor after a 1.5 second warning, so jump it), interference clouds in the Wi-Fi tickets (a jammer cuts a stretch on a rhythm, so run through the gap), rogue-AP decoys in the security tickets (red fake access points with a “?” that you can stomp for +80, while real devices are solid and safe) and a ghost of your best run that you can race.
What is the glowing pipe
A purple pipe with a “?” hides a bonus stage in most arcade tickets. Stand on it and hold ↓: for 20 seconds you move a network card with ← → and catch falling packets. Green 200 OK packets give points, gold ones give more, malformed grey ones give nothing and only reset your streak (five good ones in a row double the points). There is no penalty, you can leave early with Esc, and each ticket allows one visit.
Are there badges and a daily challenge
Yes. After an arcade ticket you can earn Five nines (no hit), Collector (every coin), Speedrunner (fast finish) and Stomp streak (three stomps in a row) and Packet catcher (at least 15 good packets in the bonus stage). They are saved in your browser. In the Pet networks launcher the Today button fills in a date code, so everybody gets the same scenario that day.
Is there an easier arcade mode
Yes: Relaxed. Switch it on under Pace on the title screen or in the pause menu (Jump & run only). Bugs, zap arms and storm waves move slower, lasers and jammers are on for less time, and a hit is just a bump: you never lose an SLA nine, there is no outage and falling into a pit costs no points. To keep the high scores fair, relaxed runs are not listed there and earn no badges or ghost. Puzzle only and Training are not affected.
Can I configure a firewall the ASA way
Yes. On a firewall, ssh to it and enter configuration mode. Select an interface with interface eth0 and give it a name and a trust level: nameif inside, security-level 100. Rules are named access lists: access-list FW_POLICY extended permit tcp host 10.1.1.10 host 10.2.2.20 eq https; add line 1 to insert at a position, range 49152 65535 for a port range, and no access-list … with the same text to delete a rule. access-group FW_POLICY global applies the list. Check your work with show access-list, show nameif and show conn. The simulation uses one ordered rule list per firewall, so security-level and access-group are recorded and shown, but do not change which packets pass. Objects, NAT and policy maps are recognised and marked as not simulated. The older numbered form (access-list 3 permit tcp …) still works.
How do I delete my player sign
On the title screen, in the pause menu or in the high-score window, use delete initials next to your sign. It removes the sign and your own entries in the high-score table of this browser; you are anonymous afterwards and the game stops asking for initials. Tickets and progress stay (use reset progress to start over). Scores you already sent to the shared table on netwho.ch stay there until the site owner removes them by hand: choose Delete and ask for removal in the dialog. Only the browser that created the sign can ask, and because it is done by hand it may take some time. To speed it up, or if you no longer have that browser, write to walter.hofstetter [at] netwho.com (replace “[at]” with @) or post it on the Discord channel. Anybody can type the same three letters later: signs are not accounts and cannot be reserved.
Do I need an account?
No. High-score initials are optional and are three letters.
Which languages are available?
English, German, French and Italian. Use the EN · DE · FR · IT buttons at the top right of the title screen (or at the bottom of the pause menu). The first visit follows your browser language and your choice is remembered. Menus, ticket stories, reports, help and the Training teacher are translated; the device configuration windows, the SSH terminal and the capture analyzer deliberately stay in English, because that is what real network gear looks like.
Which terminal commands work?
Press T, type ssh and a device name, then enable. Press ? at any point to see what can come next, and Tab to complete. Commands that exist on real Cisco-style gear but are not simulated appear in the list with a [not simulated] remark. In Training mode the teacher shows which show command to run before you fix a device.
What are ziplines, VPN pipes and power-up boxes?
Optional toys in the Jump & run hall. Touch a patch-cable zipline in mid-air to ride it over a pit (jump to hop off, or press ↓ to drop). Stand on a VPN pipe and hold ↓ to pop out of its twin further along. Power-up boxes give a firewall bubble (absorbs one hit), 10G boots (faster for 8 seconds) or a coin magnet (10 seconds).
Which version am I playing?
The version and release date are shown at the bottom of the title screen and of the pause menu.
Is progress saved?
Yes, in your browser (unlocked tickets, best scores, settings). Clearing the site data resets it. The iPhone and iPad app keeps its progress on the device.
Why is my run not in the high scores?
Runs with help (H), puzzle-only runs and “unlock all devices” runs are not listed.
I found a bug, or I have an idea for a ticket.
Please write to me via the contact page. Screenshots and the ticket number help.