- About
- Play
- How a turn works
- The four gauges
- Actions
- Global controls
- What counters what
- Hunters
- The 10 cases
- Strategy
- Feedback
About
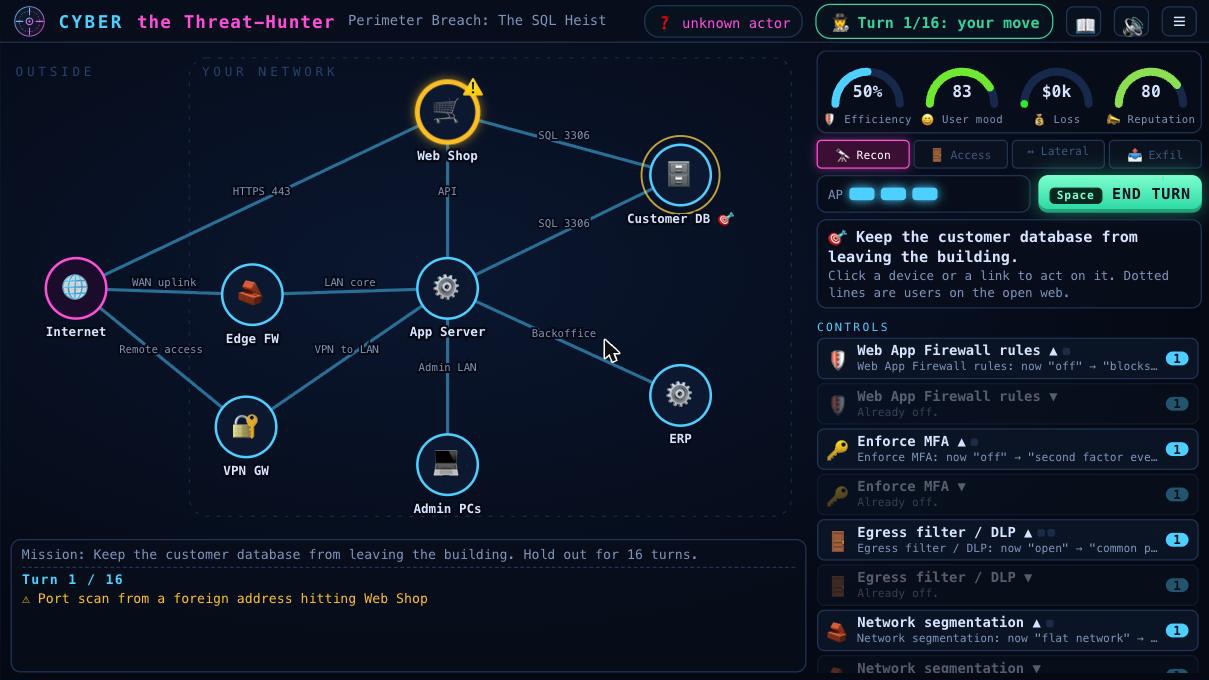
Cyber the Threat-Hunter is a turn-based “catch the hacker” game and a sibling of Ping the Networker. You are Cyber, the SOC lead. An attacker is somewhere in your network, you cannot see him directly, and every move you make costs something: user patience, money or reputation. The game is meant to teach how detection, response and security controls trade off against each other, not to be a simulation of any one product.
Status: fully QA’d in the browser. There is no iOS app yet.
Feedback and bug reports are very much appreciated. See Feedback below.
Play
- Works in any current desktop browser. The layout adapts to phones, in portrait and landscape.
- No account and no installation. Optional 3-letter initials for the high-score table.
- Keys: Space end turn · M sound on/off · Esc menu · Del deselect.
How a turn works
- The hunter moves first. He takes one action: recon, exploit, move laterally or exfiltrate. Each action makes some noise, and your sensors turn noise into ⚠ alerts. Some alerts are false alarms.
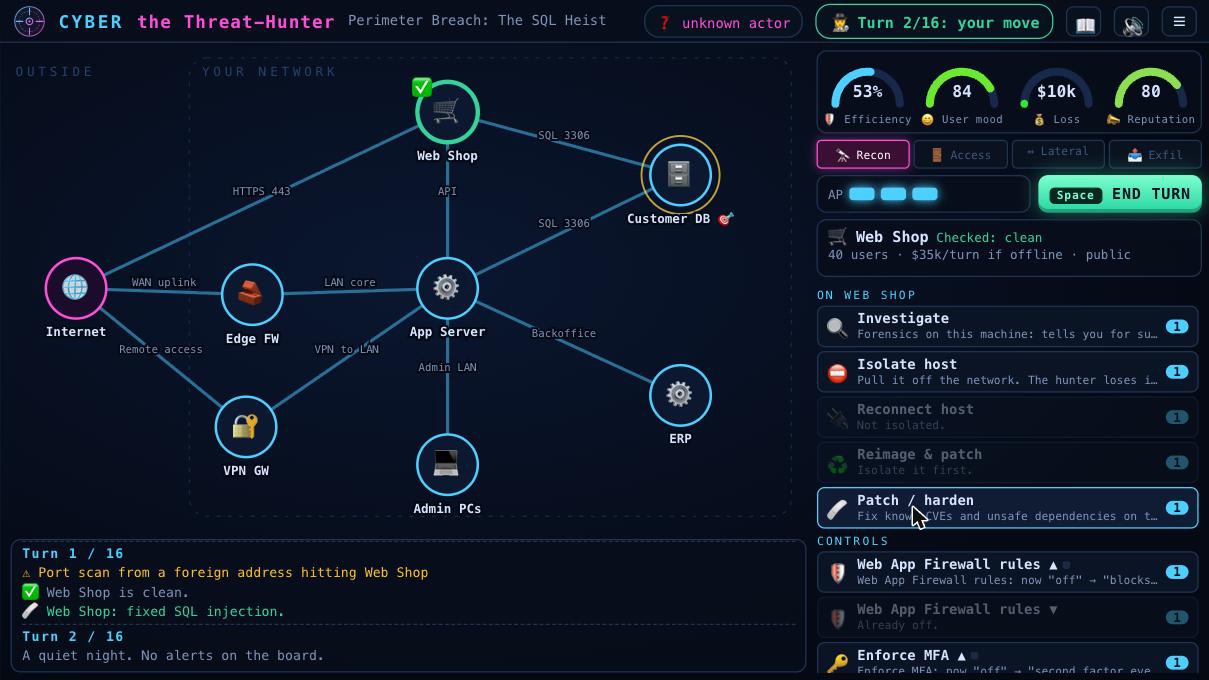
- You get 3 action points (AP). Click a device or a link, then choose what to do with it. Global controls (MFA, WAF, egress filtering and so on) change the odds for the whole network.
- Upkeep. Strict controls, offline systems and active intruders cost mood, money and reputation every turn.
- Repeat for 16 turns. The hunter may also give up after 3 turns without a viable target.
Fog of war
The hunter’s real position is hidden. You see alerts (some of them false), kill-chain stages once you have evidence, and what you confirm with 🔍 investigate. The chip at the top shows the attacker as “unknown actor” until you confirm a compromise. Practice mode (checkbox on the menu) shows hostile hosts and logs every hunter move, which is the best way to learn, but it is not ranked.
Winning and losing
- You win by surviving all turns, or by leaving the hunter with nothing to attack.
- You lose if 100 % of the crown jewels are exfiltrated (30 % per turn, slowed by egress filtering), if user mood hits zero (mutiny), if reputation hits zero, or if the financial loss reaches $5 M.
The four gauges
| Gauge | What moves it | Ends the game at |
|---|---|---|
| 🛡 Efficiency | Up for confirming and isolating real intruders. Down for isolating clean hosts, active intruders and exfiltration | Part of the final score |
| 🙂 User mood | Strict controls cost mood every turn, as do isolated hosts and cut links. Recovers +3 per turn. Below 35, users create shadow IT and all your controls become 40 % weaker | 0 = mutiny |
| 💰 Financial loss | Actions, offline revenue, active intruders, exfiltration | $5 M |
| 📣 Reputation | Down for exfiltration and public-facing systems being offline. Up for a well-timed public statement | 0 |
Actions
On a device
| Action | What it does |
|---|---|
| 🔍 Investigate | Forensics on one machine: tells you for sure whether it is compromised. This is how you separate real alerts from false ones |
| ⛔ Isolate host | Pulls it off the network. The hunter loses it, but so do your users and your revenue |
| 🔌 Reconnect host | Brings an isolated host back |
| ♻️ Reimage & patch | Wipes an isolated host and fixes it for good. Isolate it first |
| 🩹 Patch / harden | Fixes known CVEs and unsafe dependencies on the host without taking it offline |
| ✂️ Cut a link | Removes a connection between two systems, such as an uplink or a VPN tunnel |
Operations
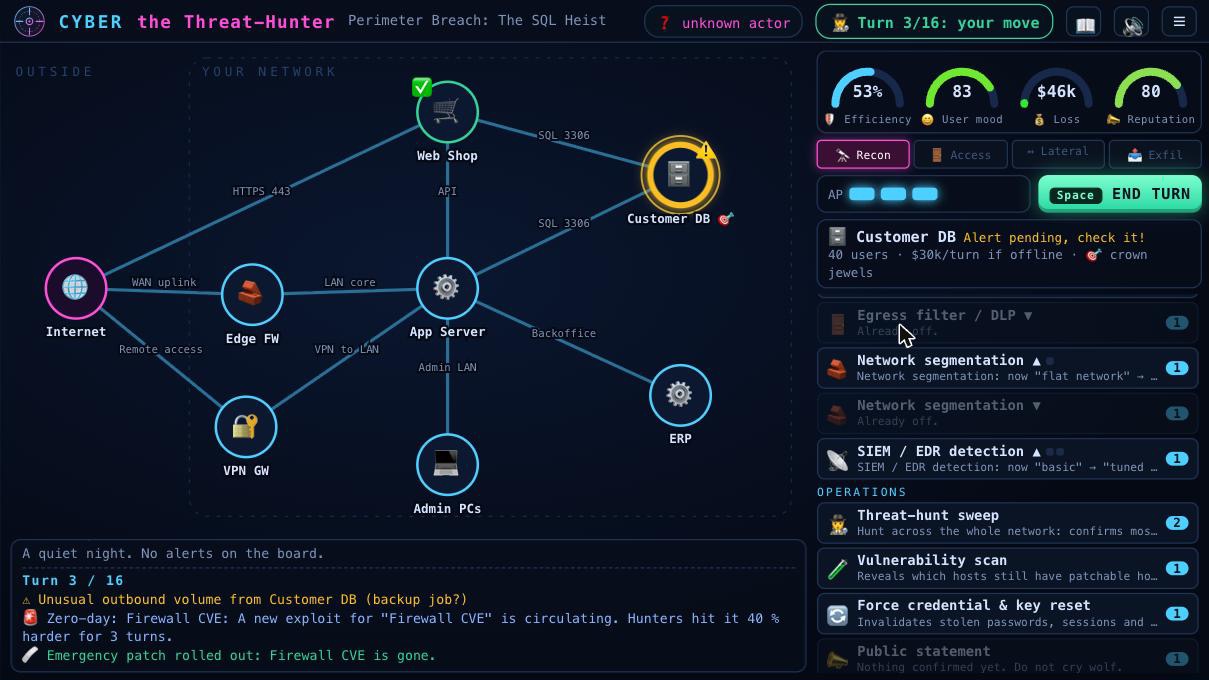
- Threat-hunt sweep (2 AP): hunts across the whole network and confirms the most suspicious hosts.
- Vulnerability scan: shows which hosts still have patchable holes.
- Force credential & key reset: invalidates stolen passwords, sessions and keys.
- Public statement: repairs reputation, but only once something has been confirmed. Do not cry wolf.
Global controls
Controls apply to the whole network. Most can be raised (▲) or lowered (▼). Stronger controls help, but they cost mood and money, and some also cost an upkeep every turn.
| Control | Effect |
|---|---|
| 🛡️ Web App Firewall rules | Blocks SQL-injection patterns, with some false blocks |
| 🔑 Enforce MFA | Second factor everywhere. Counters weak credentials |
| 🧭 URL / proxy filter | Blocks malware and phishing categories, or goes to allow-list only |
| 🚪 Egress filter / DLP | Limits what can leave. Slows exfiltration |
| 🧱 Network segmentation | Micro-segments and internal ACLs. Makes lateral movement harder |
| 📬 Mail sandbox & link rewrite | Detonates attachments and rewrites links |
| 🎓 Awareness campaign | An e-mail and a poster, or real phishing drills |
| 🗝️ Least-privilege review | Need-to-know access. Counters insiders with valid credentials |
| 🧯 Virtual patch | An IPS rule, or an exposed feature switched off at the edge. Useful when no vendor patch exists yet |
| ☎️ Help-desk call-back | Identity is verified before any reset |
| 🌍 Conditional access | Only managed devices and known networks |
| 💾 Immutable offline backups | Air-gapped, tested restores. Slows ransomware encryption |
| 📡 SIEM / EDR detection | Basic, tuned, or paranoid rules (more alerts, and more false alarms) |
What counters what
| Weakness | Counter |
|---|---|
| Firewall, VPN or supply-chain CVEs, SQL injection | Patch the host. A WAF also blunts SQL injection |
| Weak credentials | MFA |
| Phishing | Mail sandbox, awareness, URL filter |
| Drive-by downloads | URL filter |
| Insider with valid credentials | Least privilege |
| Lateral movement (no vulnerability, just an internal pivot) | Segmentation |
| Data exfiltration | Egress filter / DLP, or cutting links |
The hunters
| Type | Behaviour |
|---|---|
| 🧒 Script kiddie | Loud. Easy to detect, easy to stop |
| 🥷 APT | Quiet and patient. Few alerts, so you need to hunt |
| 💣 Ransomware crew | Fast. Egress filters do not help; backups do |
| 📢 Hacktivist | Goes for reputation damage |
Unless you choose one on the menu, the hunter is random and unknown until you confirm a compromise. The hunter’s sprite only travels on the map when you detected his move; an undetected move is a faint blip at the Internet node.
The 10 cases
Classic cases
| Case | The story |
|---|---|
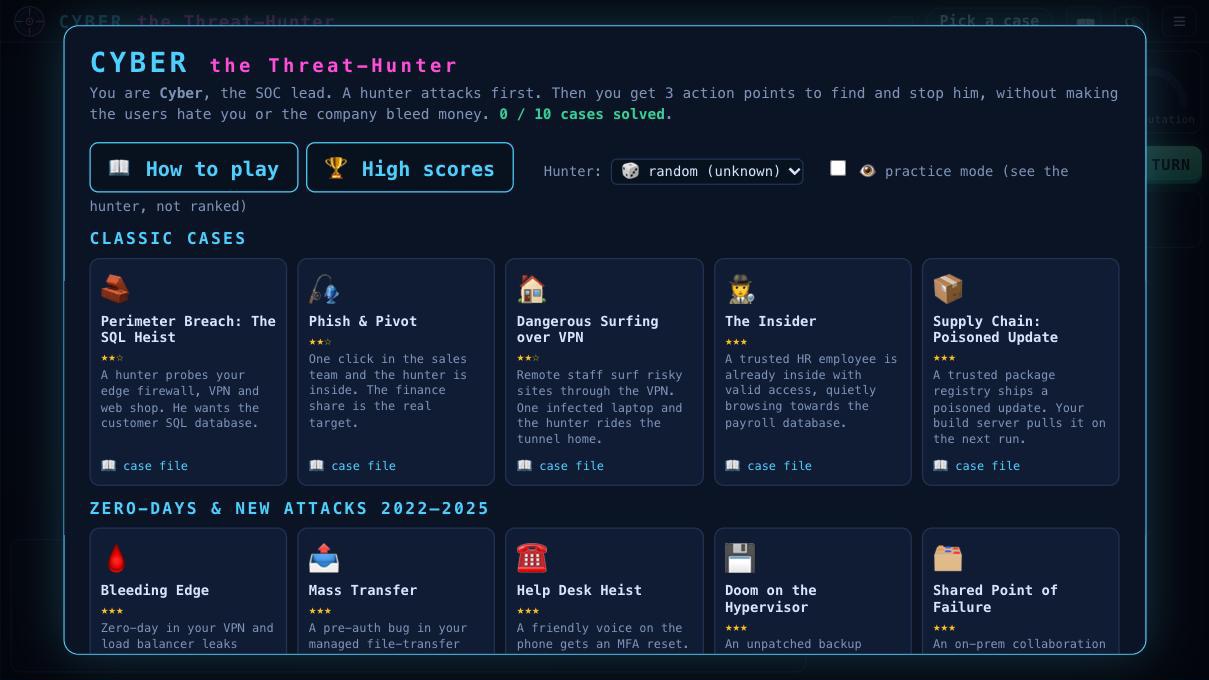
| Perimeter Breach: The SQL Heist | Firewall and VPN CVEs and a SQL-injectable web shop. The hunter wants the customer database |
| Phish & Pivot | One click in the sales team, an Active Directory pivot, and the finance share as the real target |
| Dangerous Surfing over VPN | Remote staff surf risky sites through the VPN. One infected laptop and the hunter rides the tunnel home |
| The Insider | A trusted HR employee already has valid access and browses quietly towards the payroll database |
| Supply Chain: Poisoned Update | A trusted package registry ships a poisoned update. Your build server pulls it on the next run |
Zero-days and new attacks, 2022 to 2025
These cases are inspired by public reporting and add new mechanics.
| Case | Inspired by | New mechanic |
|---|---|---|
| 🩸 Bleeding Edge | Citrix Bleed, Ivanti Connect Secure | Zero-day: no vendor patch for several turns. Use a virtual patch. MFA does not stop session theft |
| 📤 Mass Transfer | MOVEit, GoAnywhere, Cleo | Mass-exploited pre-auth SQL injection, webshell persistence, extortion |
| ☎️ Help Desk Heist | Scattered Spider, MFA fatigue attacks | Social engineering. Call-back verification and conditional access |
| 💾 Doom on the Hypervisor | ESXiArgs, Veeam, ESXi ransomware | Management-plane segmentation. Immutable backups slow the encryption clock |
| 🗂️ Shared Point of Failure | SharePoint “ToolShell” | A patch does not evict the attacker: a key reset or reimage is required |
Random events
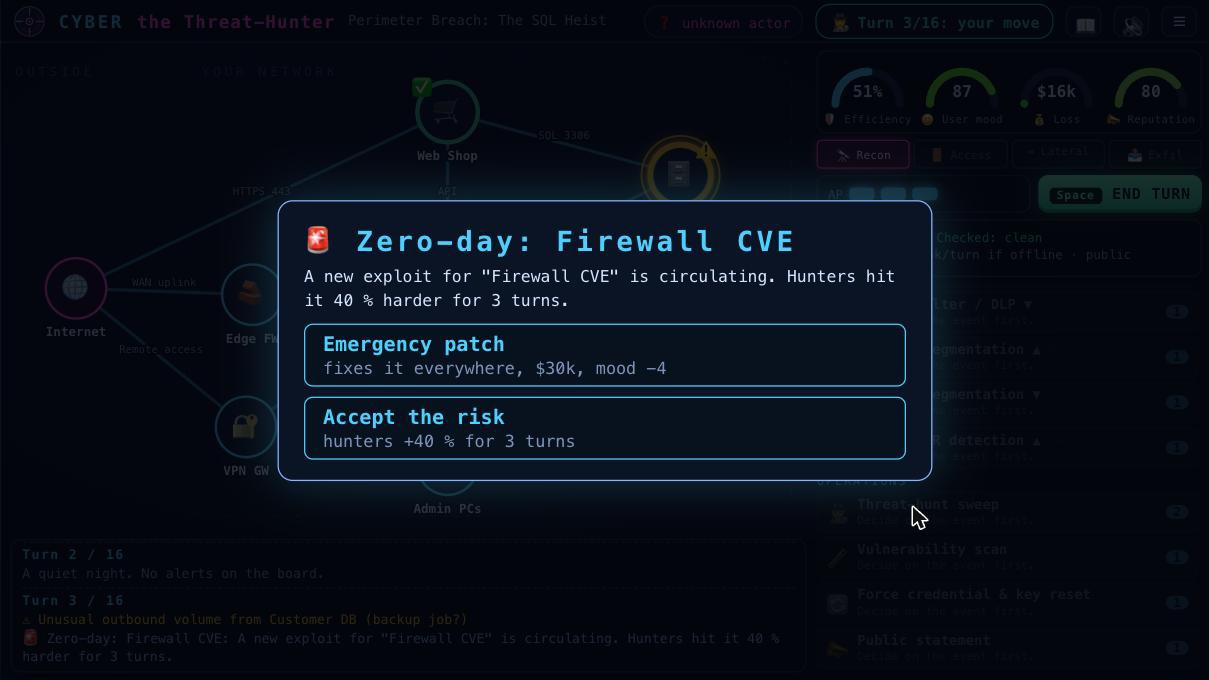
From turn 2 on, roughly one turn in three brings an event. Some are decisions (a CEO favour, a zero-day, a journalist, a free pentest) that block your turn until you answer. Others are surprises (an audit, a tip, a budget change, a marketing campaign, a help-desk flood).
Strategy
Learn first
- Play your first case in practice mode. You see the hunter and every move he makes, so you learn which of your actions actually change the outcome.
- Read the 📖 case file before a hard case. It names the weakness and the intended counter.
Spend your 3 AP well
- Investigate before you isolate. Isolating a clean machine costs efficiency, mood and money. A single 🔍 is cheap.
- Follow the crown jewels. The hunter is always heading for the 🎯. Alerts on or next to it matter more than alerts on the edge.
- Do not ignore the quiet turn. “No alerts” can mean an APT, not that you are safe. Use a threat-hunt sweep when it is quiet for too long.
- Match the control to the weakness. The table above tells you which one. Raising every control just ends in a mutiny.
- Cut early, cut cheap. A cut link or an isolated, non-critical host costs less than letting the hunter reach the database.
Watch the gauges
- Keep mood above 35. Below that, users work around you and all your controls get 40 % weaker.
- Strict controls cost mood every turn. Raise them when the case needs them, not on turn 1.
- A public statement helps reputation, but only after something is confirmed.
- For ransomware, backups and fast isolation matter more than egress filters.
Typical mistakes
- Reacting to every alert. Some are false, and that is the point of the fog of war.
- Reimaging without isolating first.
- Maxing out MFA, URL filter and egress on turn 1 and losing your users by turn 6.
- Patching the host while a zero-day has no vendor patch yet. Use a virtual patch instead.
Feedback and bug reports
Cyber the Threat-Hunter has been through a full QA pass. Even so, every player finds something I did not, and I would be very glad to hear it.
Please tell me about bugs, a case that feels unfair or too easy, rules that are unclear, ideas for new scenarios or hunters. Use the contact page, and if you can, include the case name, the turn number and what you did. A screenshot helps.